1.7 Million Certificates Revoked in 24 Hours — Would Your Environment Survive?
Two mass revocation events in one week exposed a gap most teams don't know they have. SSL.com revoked 1.7M certificates over an MPIC flaw. Let's Encrypt ran a live drill on 3M certificates. Both revealed the same question: can your renewal pipeline respond in 24 hours?
Read more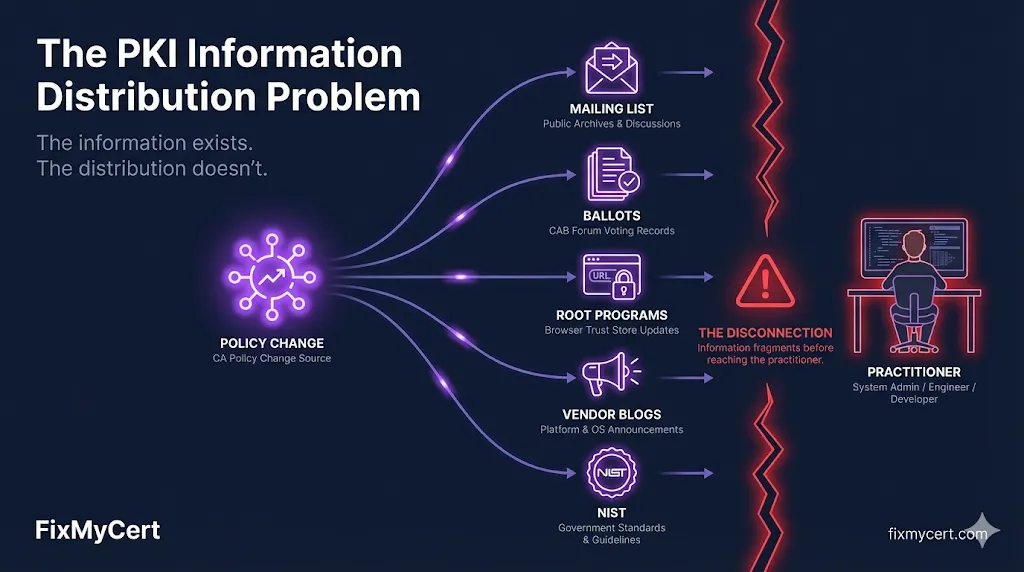
The PKI Information Distribution Problem
PKI doesn't have an information problem. It has a distribution problem. Every significant policy change gets documented somewhere — but nowhere that practitioners actually look. Here's why that's getting worse, not better.
Read more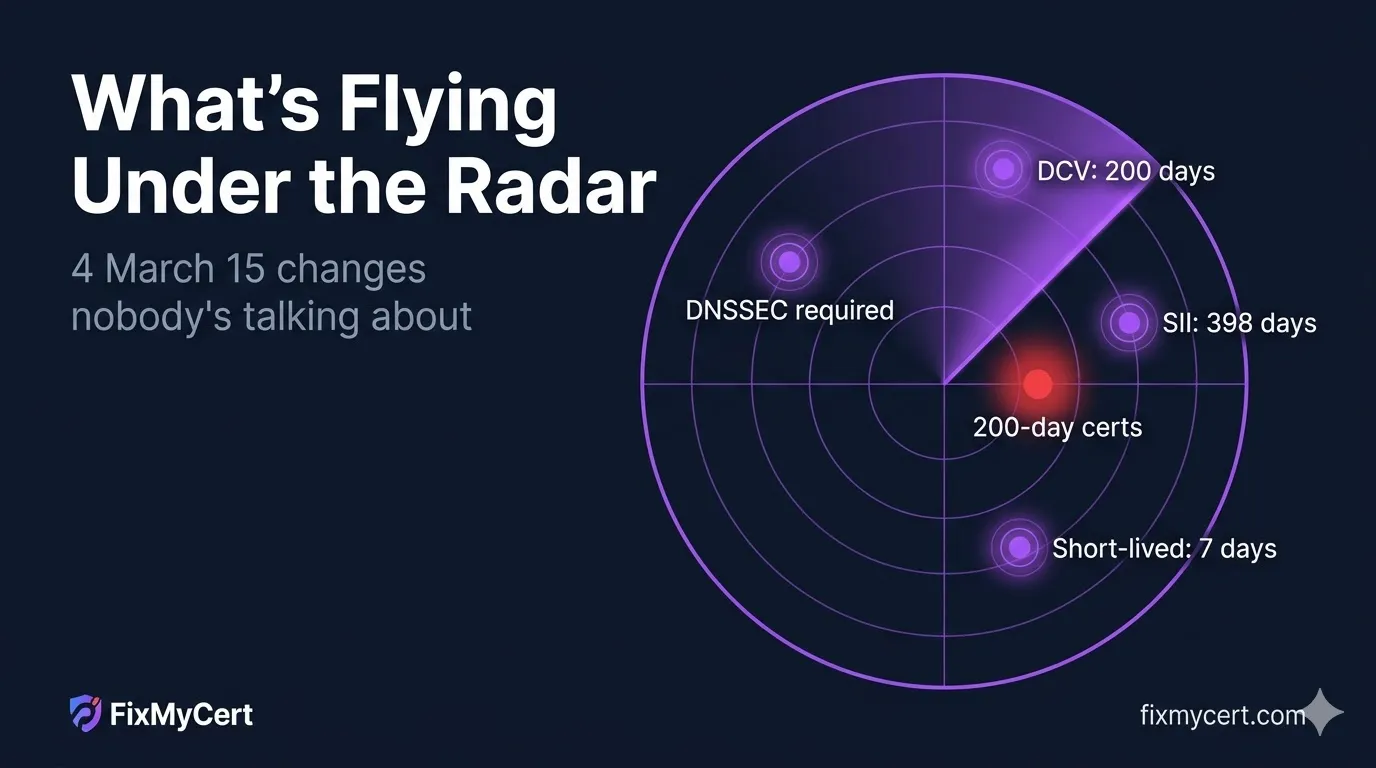
4 March 15 Changes Flying Under the Radar
Everyone's focused on 200-day certificates. Four other CA/B Forum requirements take effect the same day — DCV reuse, OV/EV validation windows, short-lived cert thresholds, and mandatory DNSSEC — and most teams aren't tracking any of them.
Read more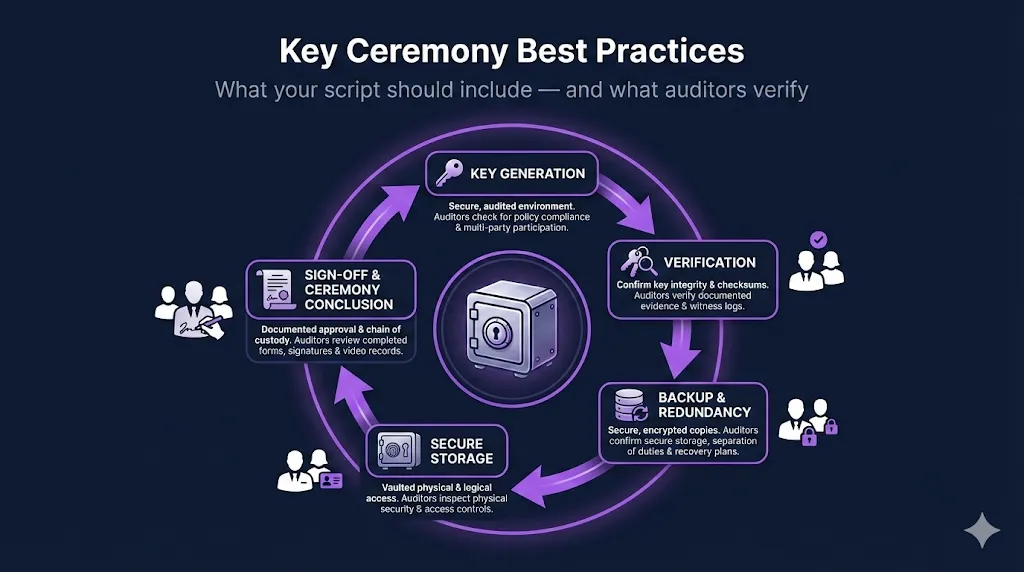
Key Ceremony Best Practices: What Your Script Should Include
A practitioner's guide to PKI key ceremony scripts — what to include, what auditors verify, and the mistakes that create findings. Includes HSM procedures, role assignments, and witness requirements.
Read more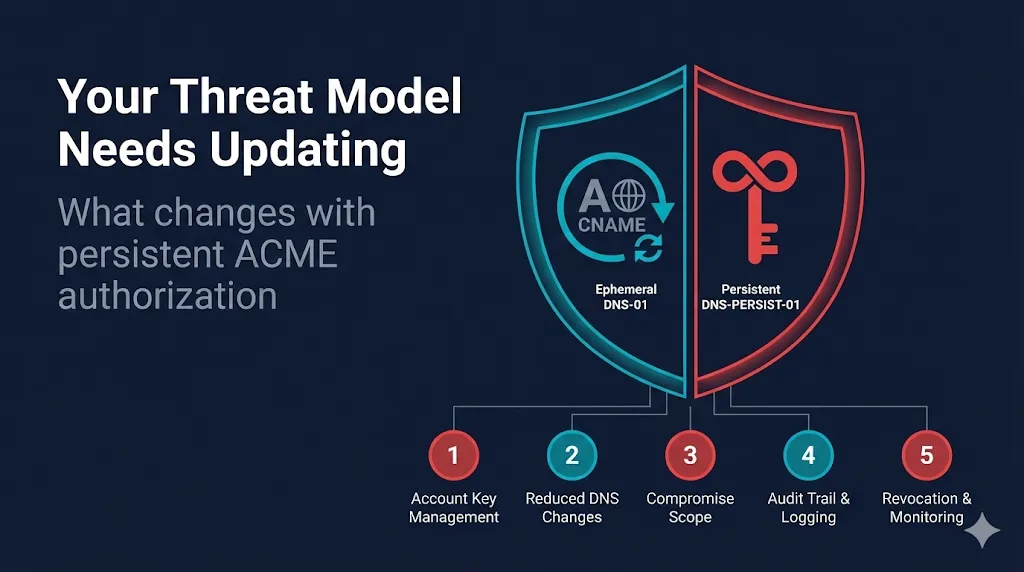
DNS-PERSIST-01 Is Great. Your Threat Model Needs Updating.
Five security assumptions that change when certificate validation becomes persistent — and what to do about each one. A practitioner-level companion to our DNS-PERSIST-01 technical guide.
Read more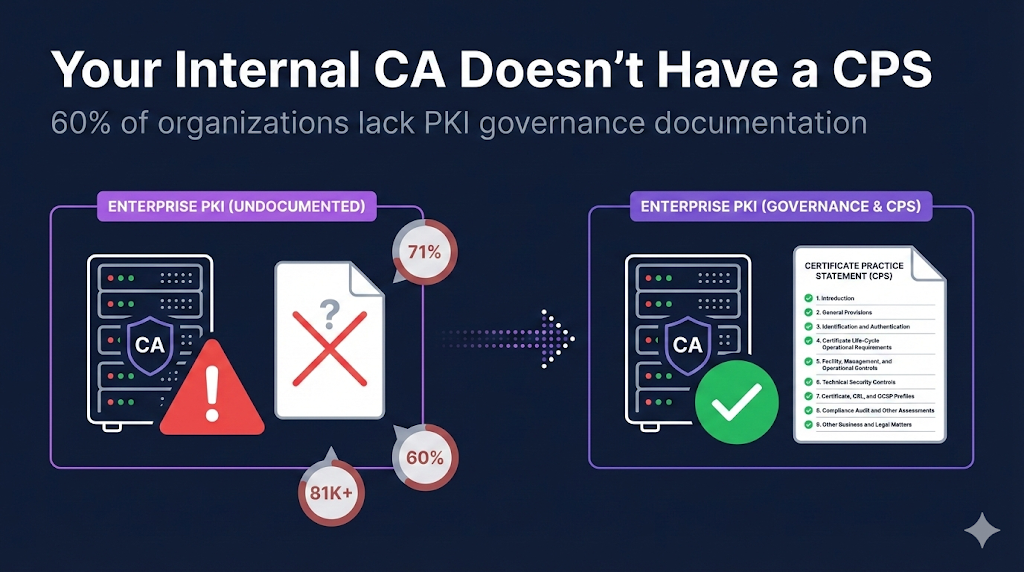
Your Internal CA Doesn't Have a CPS. Here's Why That's a Problem.
60% of organizations lack PKI governance documentation. If you're running Microsoft ADCS, EJBCA, or any private CA, you need a Certificate Practice Statement — and the RFC 3647 framework makes it easier than you think.
Read more
Your $250K Email Security Suite Just Got Beaten by a Hotmail Address
A company spends a quarter million on email security with 'Military-Grade AI,' then gets owned by a phishing email from microsft-suport-desk-real@hotmail.com. The PKI solutions to prevent this have existed for decades.
Read more