Back to Demos
43/54
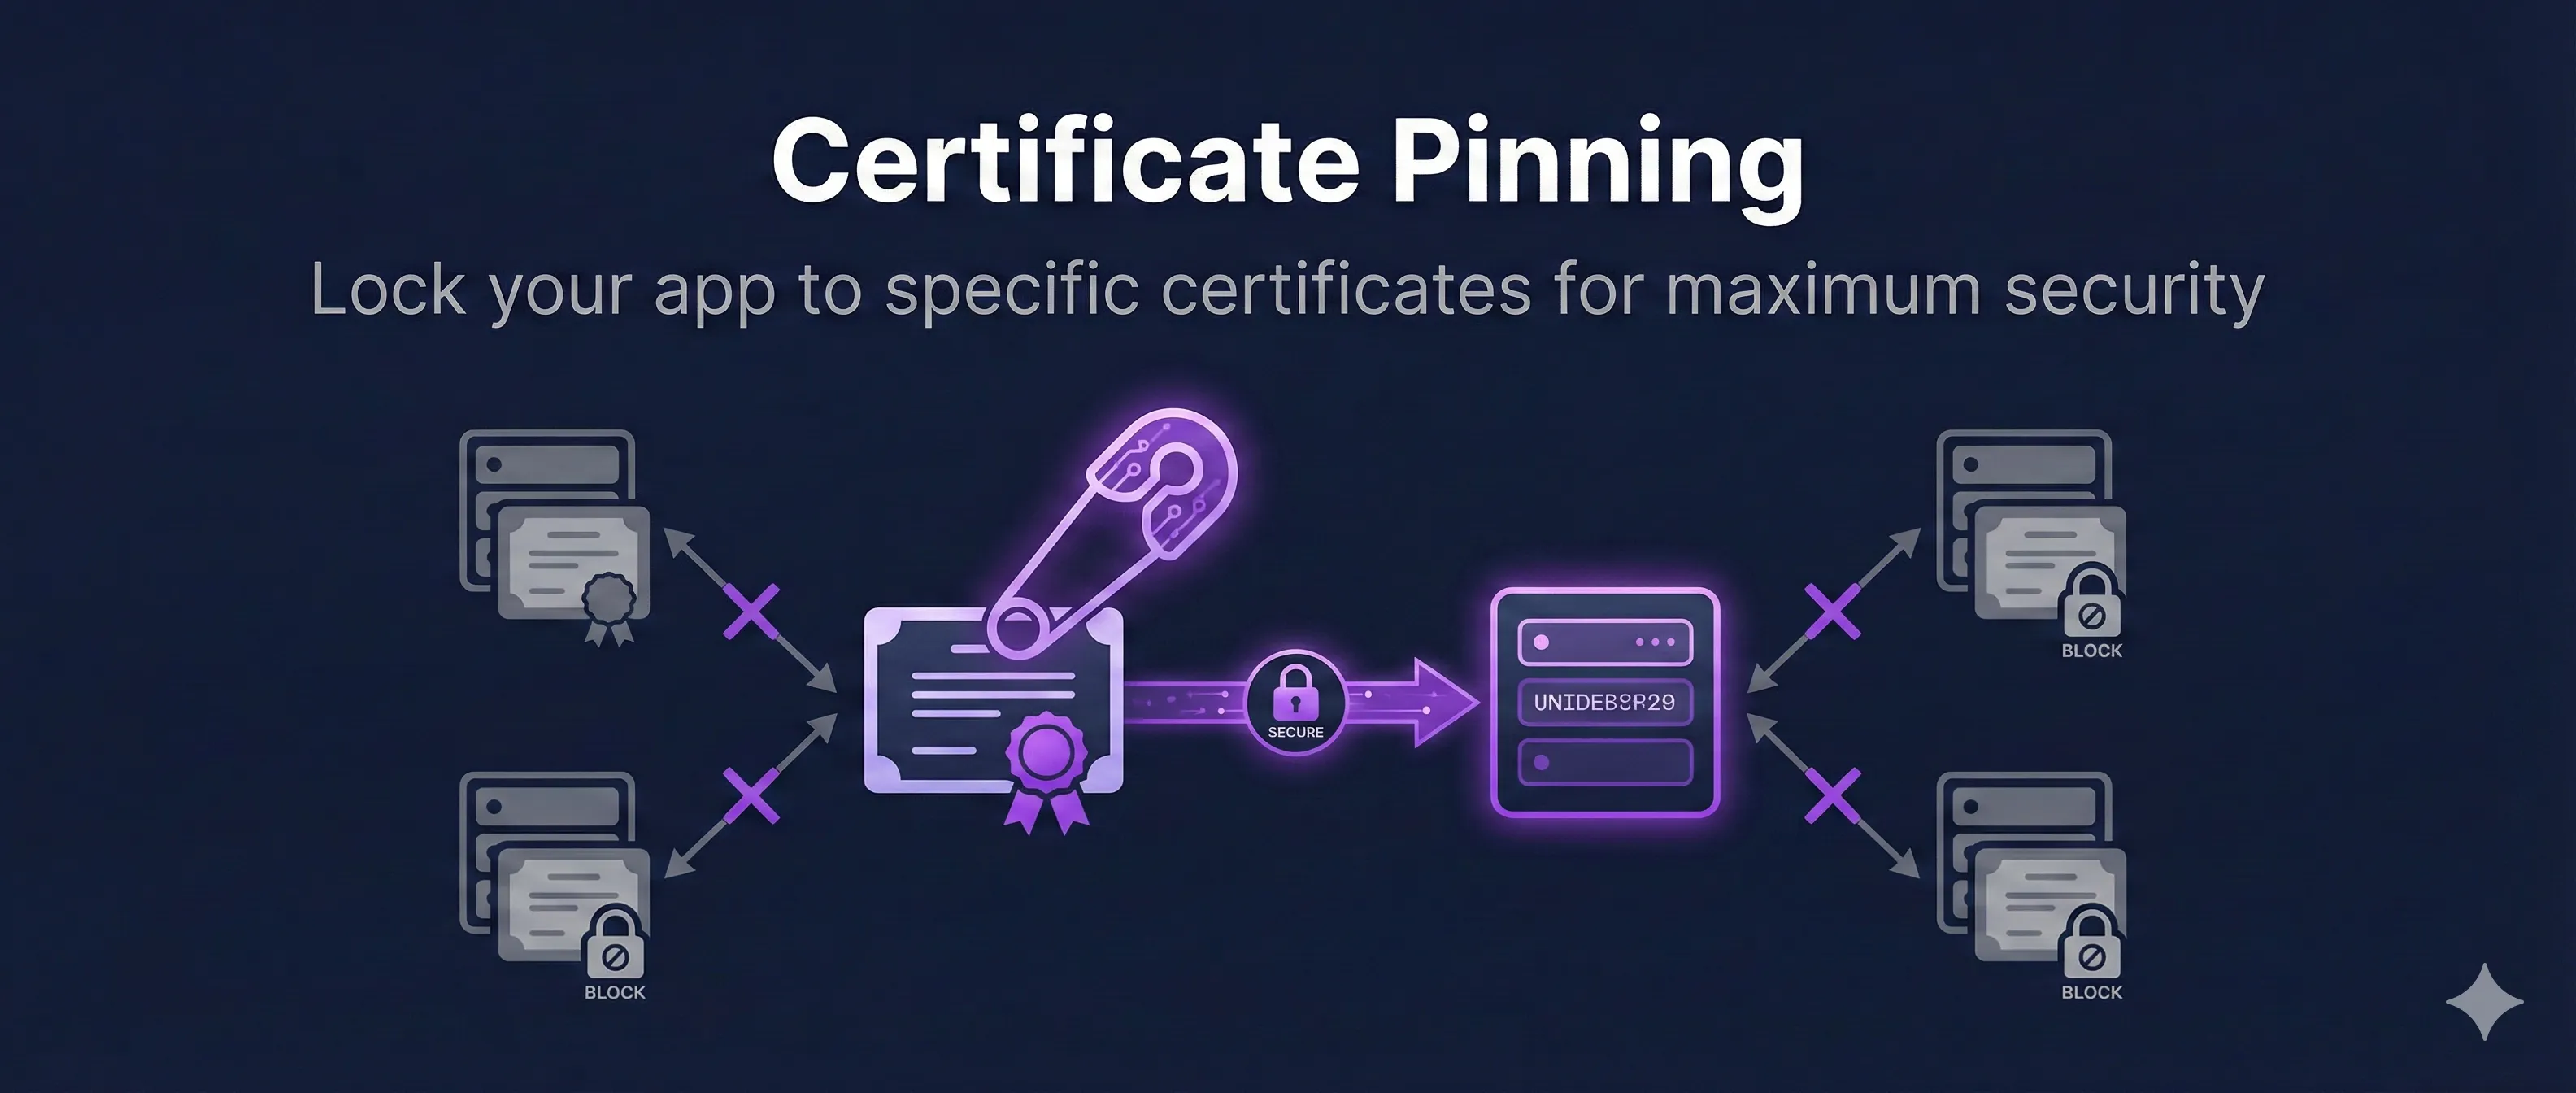
Certificate Pinning
Extra protection beyond standard CA validation for mobile apps
Normal TLS Trust
Browser trusts ANY certificate signed by ~150 CAs
DigiCert signed it? Trusted
Let's Encrypt signed it? Trusted
Random CA? ...Also trusted
Rogue CA fake cert? ...Still trusted!
Pinned TLS Trust
App trusts ONLY this specific certificate/key
Expected DigiCert cert? Trusted
Different DigiCert cert? REJECTED
Let's Encrypt cert? REJECTED
Rogue CA cert? REJECTED
Only the pinned cert works
How Pin Validation Works
Certificate pinning: Trust only what you expect, reject everything else
Want to learn more?
Read our complete guide on certificate pinning