Cert Automation Toolkit
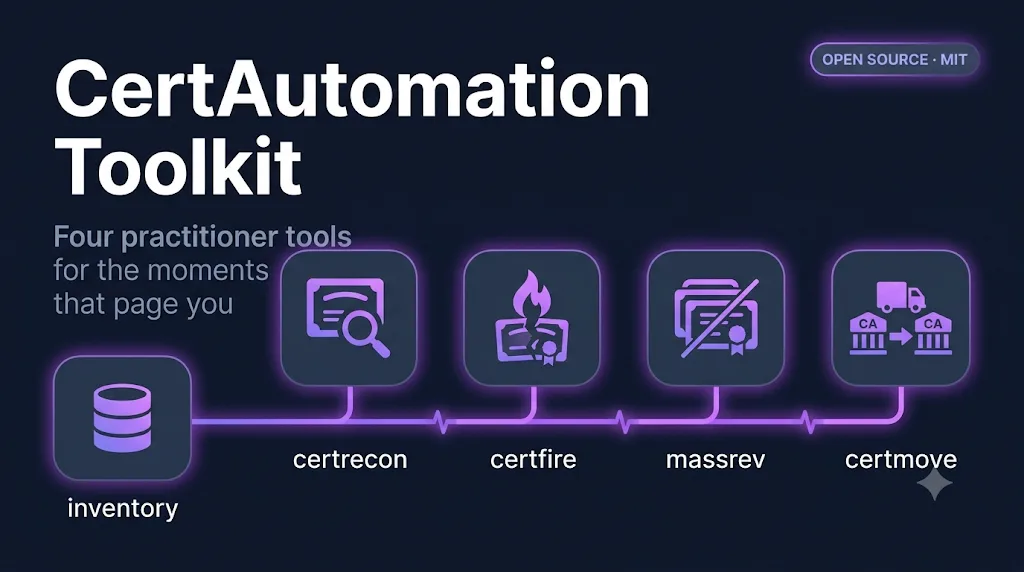
Four practitioner tools for the certificate scenarios that actually page you. Open-source, MIT-licensed, runs in your browser.
Work a full incident end to end
The Certificate War Game chains all four tools through one escalating outage — see why they work as a system, not four separate scripts.
The four scenarios
Pick the one that matches the page you got this week.
Discovery & Inventory
What certificates are out there — and which ones are already revoked?
Open scenarioOutage Response
A certificate just broke production. What is wrong and what do I do next?
Open scenarioMass Revocation Response
A CA just revoked thousands of our certificates. How do we prioritize and burn it down?
Open scenarioCA-to-CA Migration
We are switching CAs. How do we prove every endpoint actually moved?
Open scenarioThey chain together
The discovery inventory is the spine. Scan once; the rest run off it. Outage response reads it to stage replacements. Mass revocation reads it to prioritize a burndown. Migration reads it to plan and verify the move.
   ┌────────────┐    ┌────────────┐    ┌──────────────┐    ┌────────────┐
   │  certrecon │ ─► │  certfire  │    │   massrev    │    │  certmove  │
   │ discover & │    │  diagnose  │    │  prioritize  │    │  plan &    │
   │  inventory │    │  & stage   │    │  & burndown  │    │  verify    │
   └─────┬──────┘    └────────────┘    └──────┬───────┘    └─────┬──────┘
         │                                    │                  │
         └────────── shared inventory ────────┴──────────────────┘
                   ( the spine of every scenario )
Design principles
Read-only by default
Every tool defaults to inspection, not mutation. You see what is in your estate before anything in your estate changes.
Scenarios over catalogs
The toolkit is organized around the four moments that page you — not around a feature checklist that maps to no real day.
Inventory is the product
Discovery produces one artifact every other tool ingests. Scan once, then run the rest off the same spine.
47-day reality
Built for the world where certificates last 47 days and CAs revoke in batches. If your tooling assumes a 1-year cycle, it is already late.
Quick start
One dependency (cryptography), one virtualenv, and you are running.
python3 -m venv .venv
source .venv/bin/activate
pip install cryptography

# Try the first scenario
python3 01-discovery/certrecon.py inspect revoked.badssl.com:443 --check-revocation