Discovery & Inventory
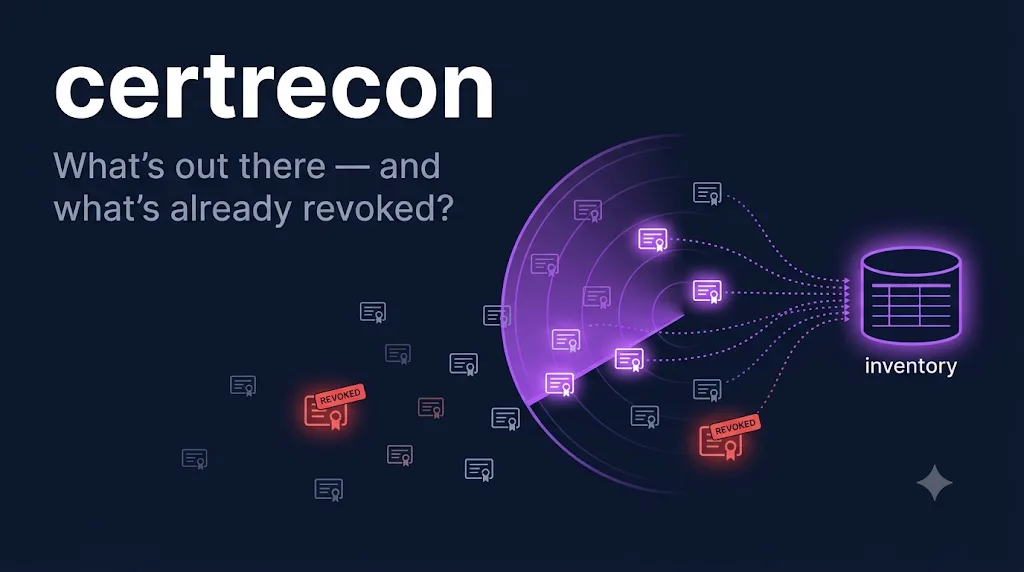
Find what you don't know about — including the ones that are already revoked.
Why this tool exists
You cannot automate what you cannot see. Discovery is the spine of every PKI program — and it is where most programs are weakest.
certrecon is a single-file Python tool that sweeps hosts, pulls each certificate, checks OCSP and CRL revocation status, and writes a clean inventory CSV. No agents, no SaaS, no telemetry leaving your network.
Run it once and you have the artifact every other tool in the toolkit needs: a row per certificate with subject, SANs, issuer, expiry, key algorithm, and — critically — revocation status. The inventory is the product.
What it does
01Inspect a single host
python3 certrecon.py inspect revoked.badssl.com:443 --check-revocationConnects, retrieves the leaf certificate, walks the chain, and queries OCSP and CRL. The REVOKED (CRL) verdict you see on the demo Repl is the strongest single screen in the toolkit — it tells you whether any production endpoint is serving a certificate the issuing CA no longer trusts.
02Sweep a target list
python3 certrecon.py sweep --targets targets.example.txt --out inventory.csv --check-revocationReads a newline-separated list of host:port targets and writes one row per certificate. This is the file every other tool in the toolkit ingests.
03Filter the inventory
python3 certrecon.py report --inventory inventory.csv --expiring-within 47Surfaces certificates that will need a renewal cycle before 47-day mandates land. Pair the output with your ACME client to size the automation gap honestly.
Sample output
Exactly what the tool writes to your terminal. No mockups — this is real output, copied verbatim.
$ python3 certrecon.py inspect revoked.badssl.com:443 --check-revocation

Host: revoked.badssl.com:443
  Subject:     CN=revoked.badssl.com
  Issuer:      CN=DigiCert SHA2 Secure Server CA
  Not Before:  2024-03-12
  Not After:   2026-03-12  (in 287 days)
  Key:         RSA-2048
  SANs:        revoked.badssl.com
  OCSP:        REVOKED  (reason: superseded)
  CRL:         REVOKED
  -> Status:   REVOKED (CRL + OCSP agree)

1 host inspected, 1 REVOKED.
badssl.com rotates its test certificates, so dates in your live run may differ from this snapshot.
Common questions
Get the tool
GitHub
Clone the repo, install one dependency, run the tool.
git clone https://github.com/patjenkinsGIT/cert-automation-toolkit.git
cd cert-automation-toolkit
pip install cryptographyDirect download
Grab the latest release zip — everything in one file.
Download v1.0.0.zipMIT-licensed. No setup notes beyond the README in the folder.