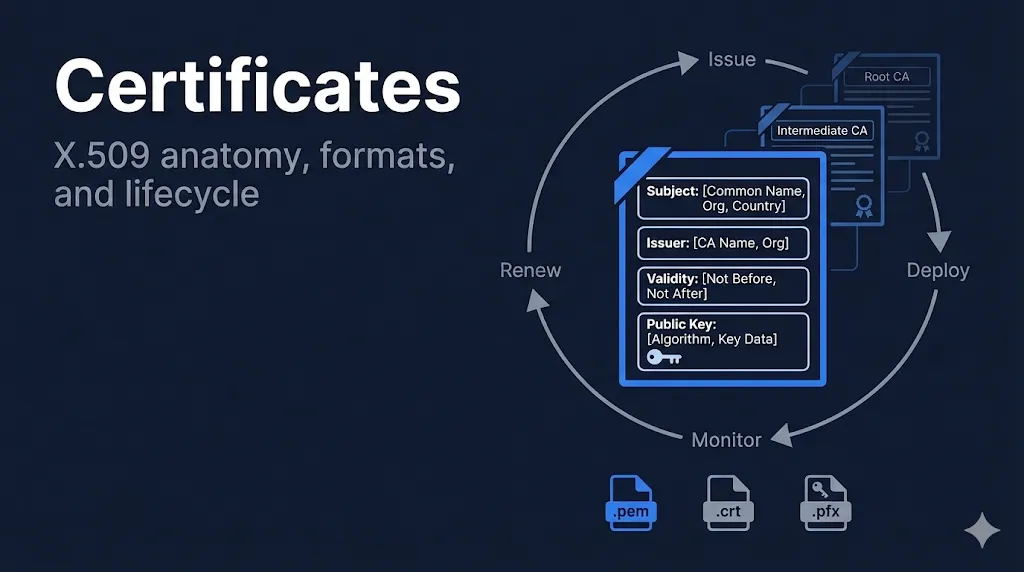
X.509 certificates, file formats, and lifecycle management. From anatomy to automation with ACME and Let's Encrypt.
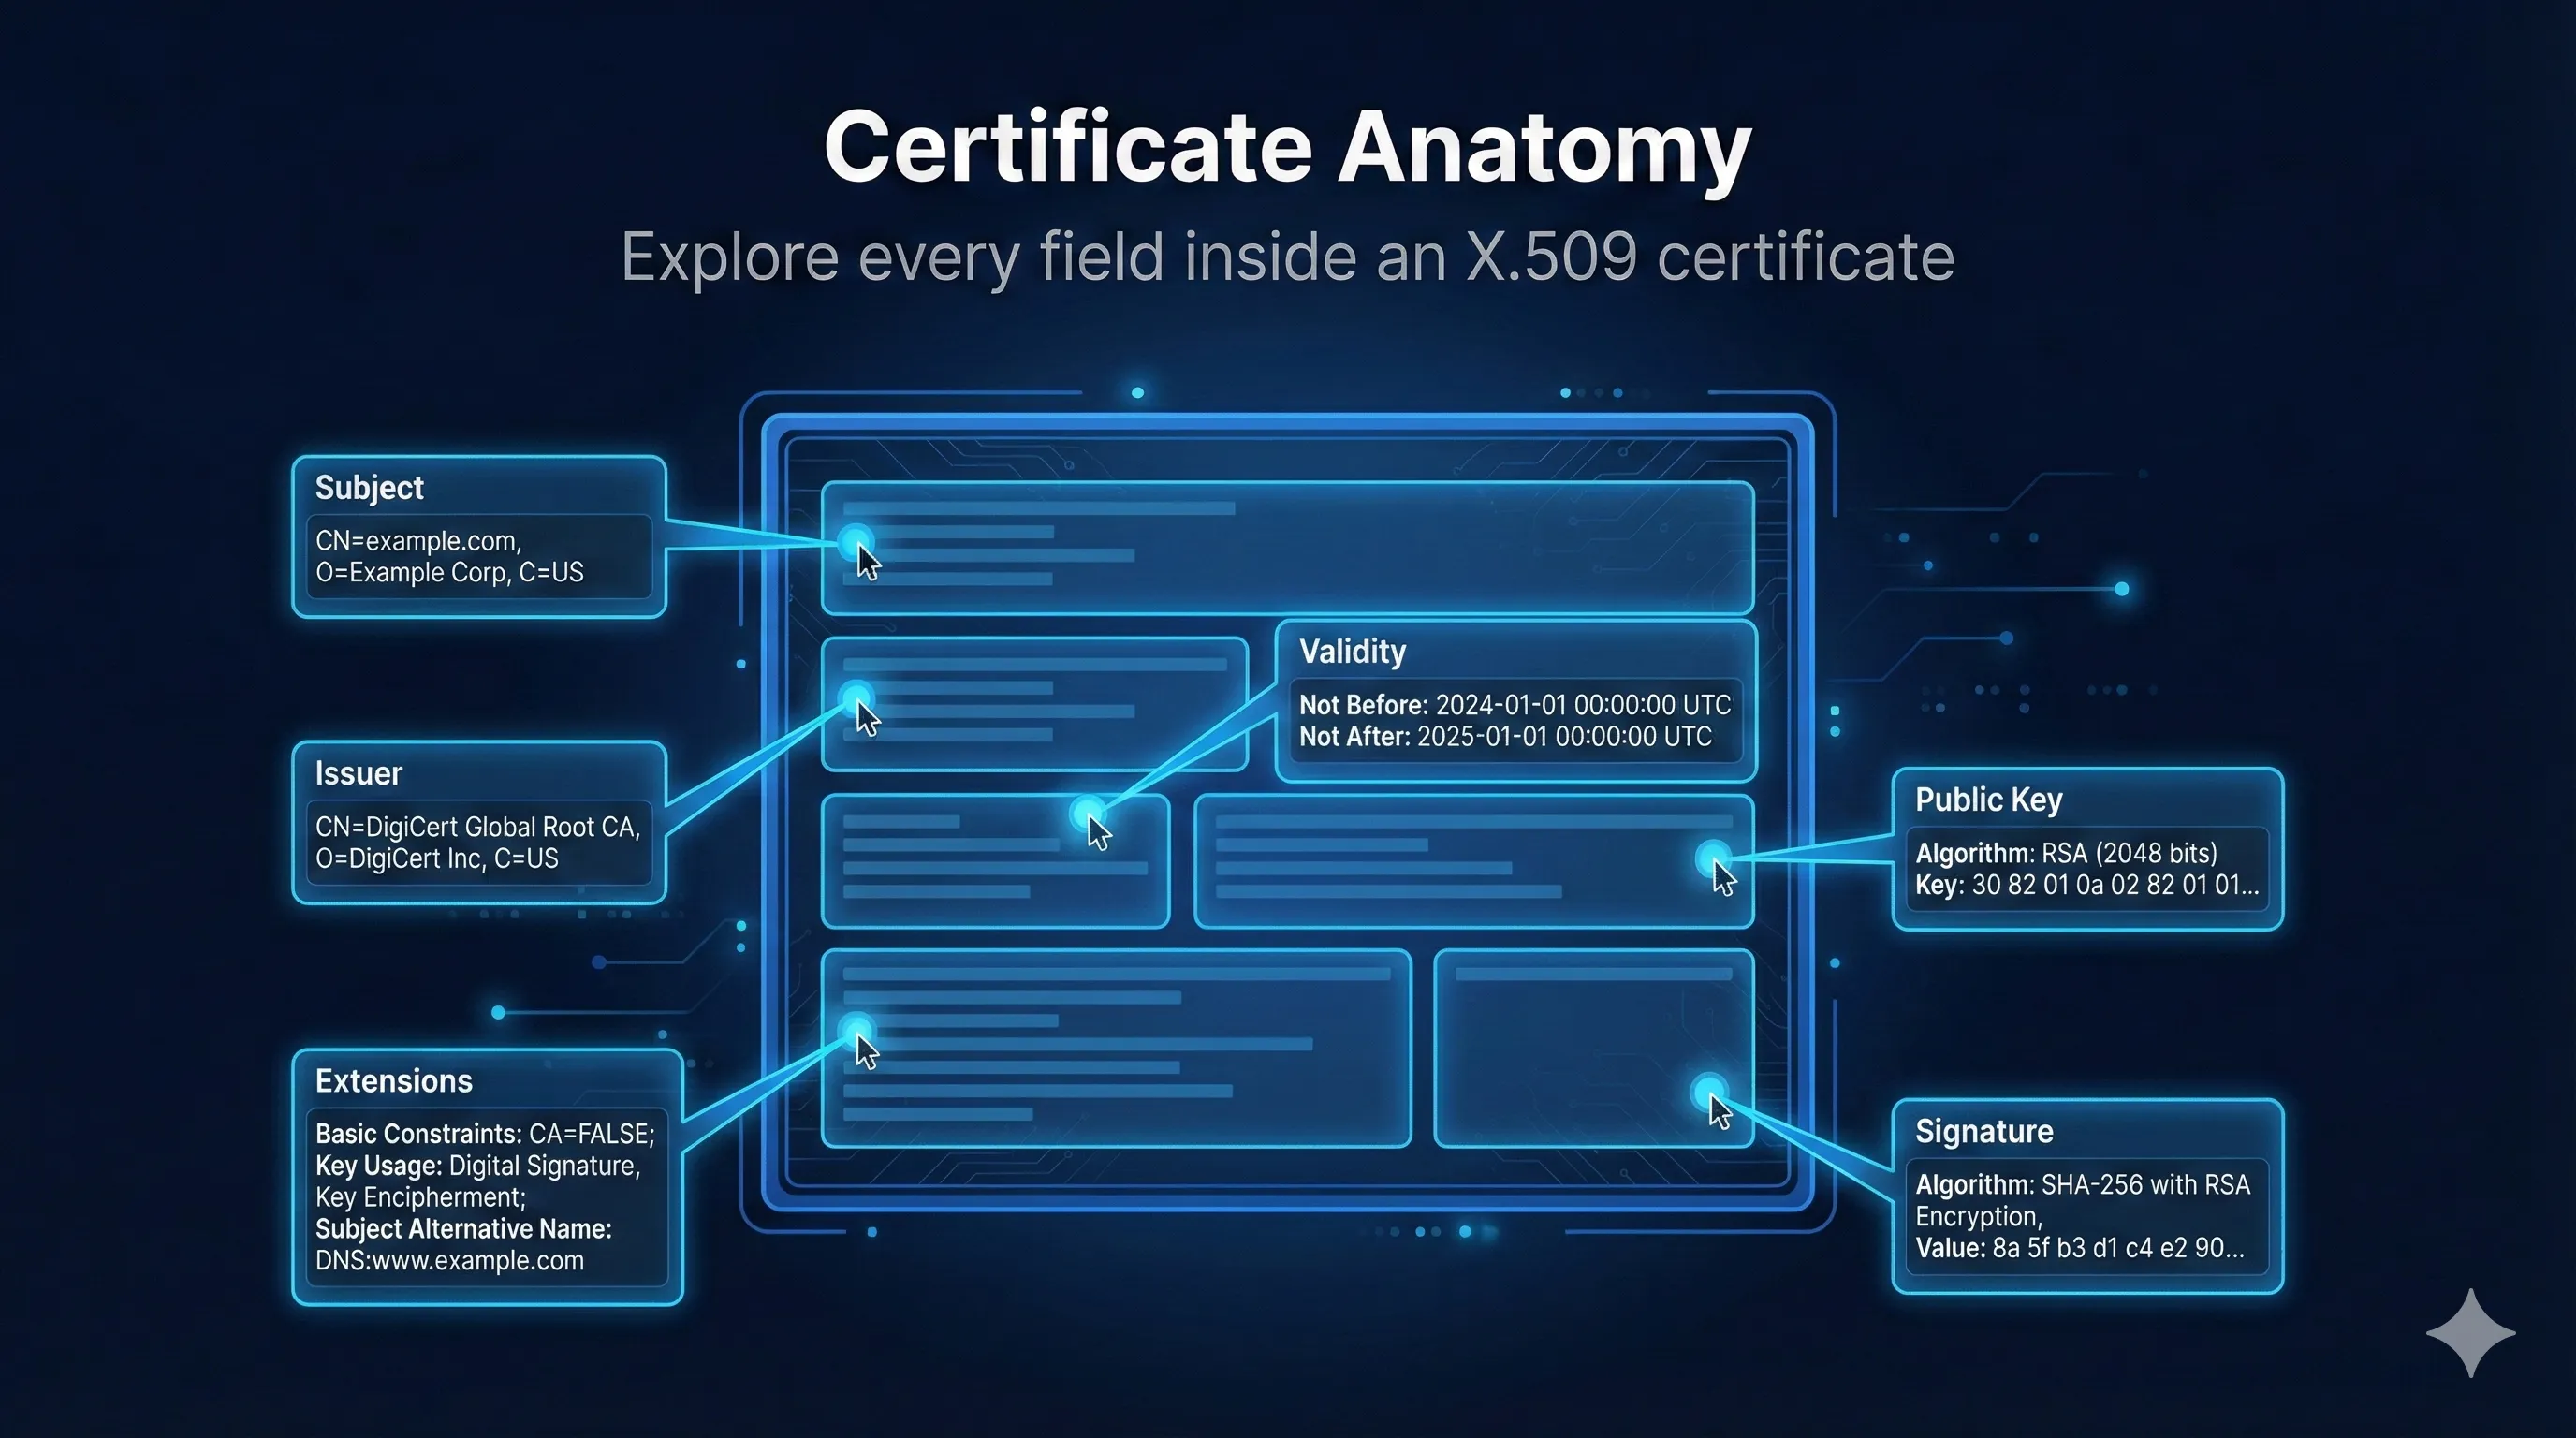
Explore every field in an X.509 certificate. Subject, issuer, extensions, and more.
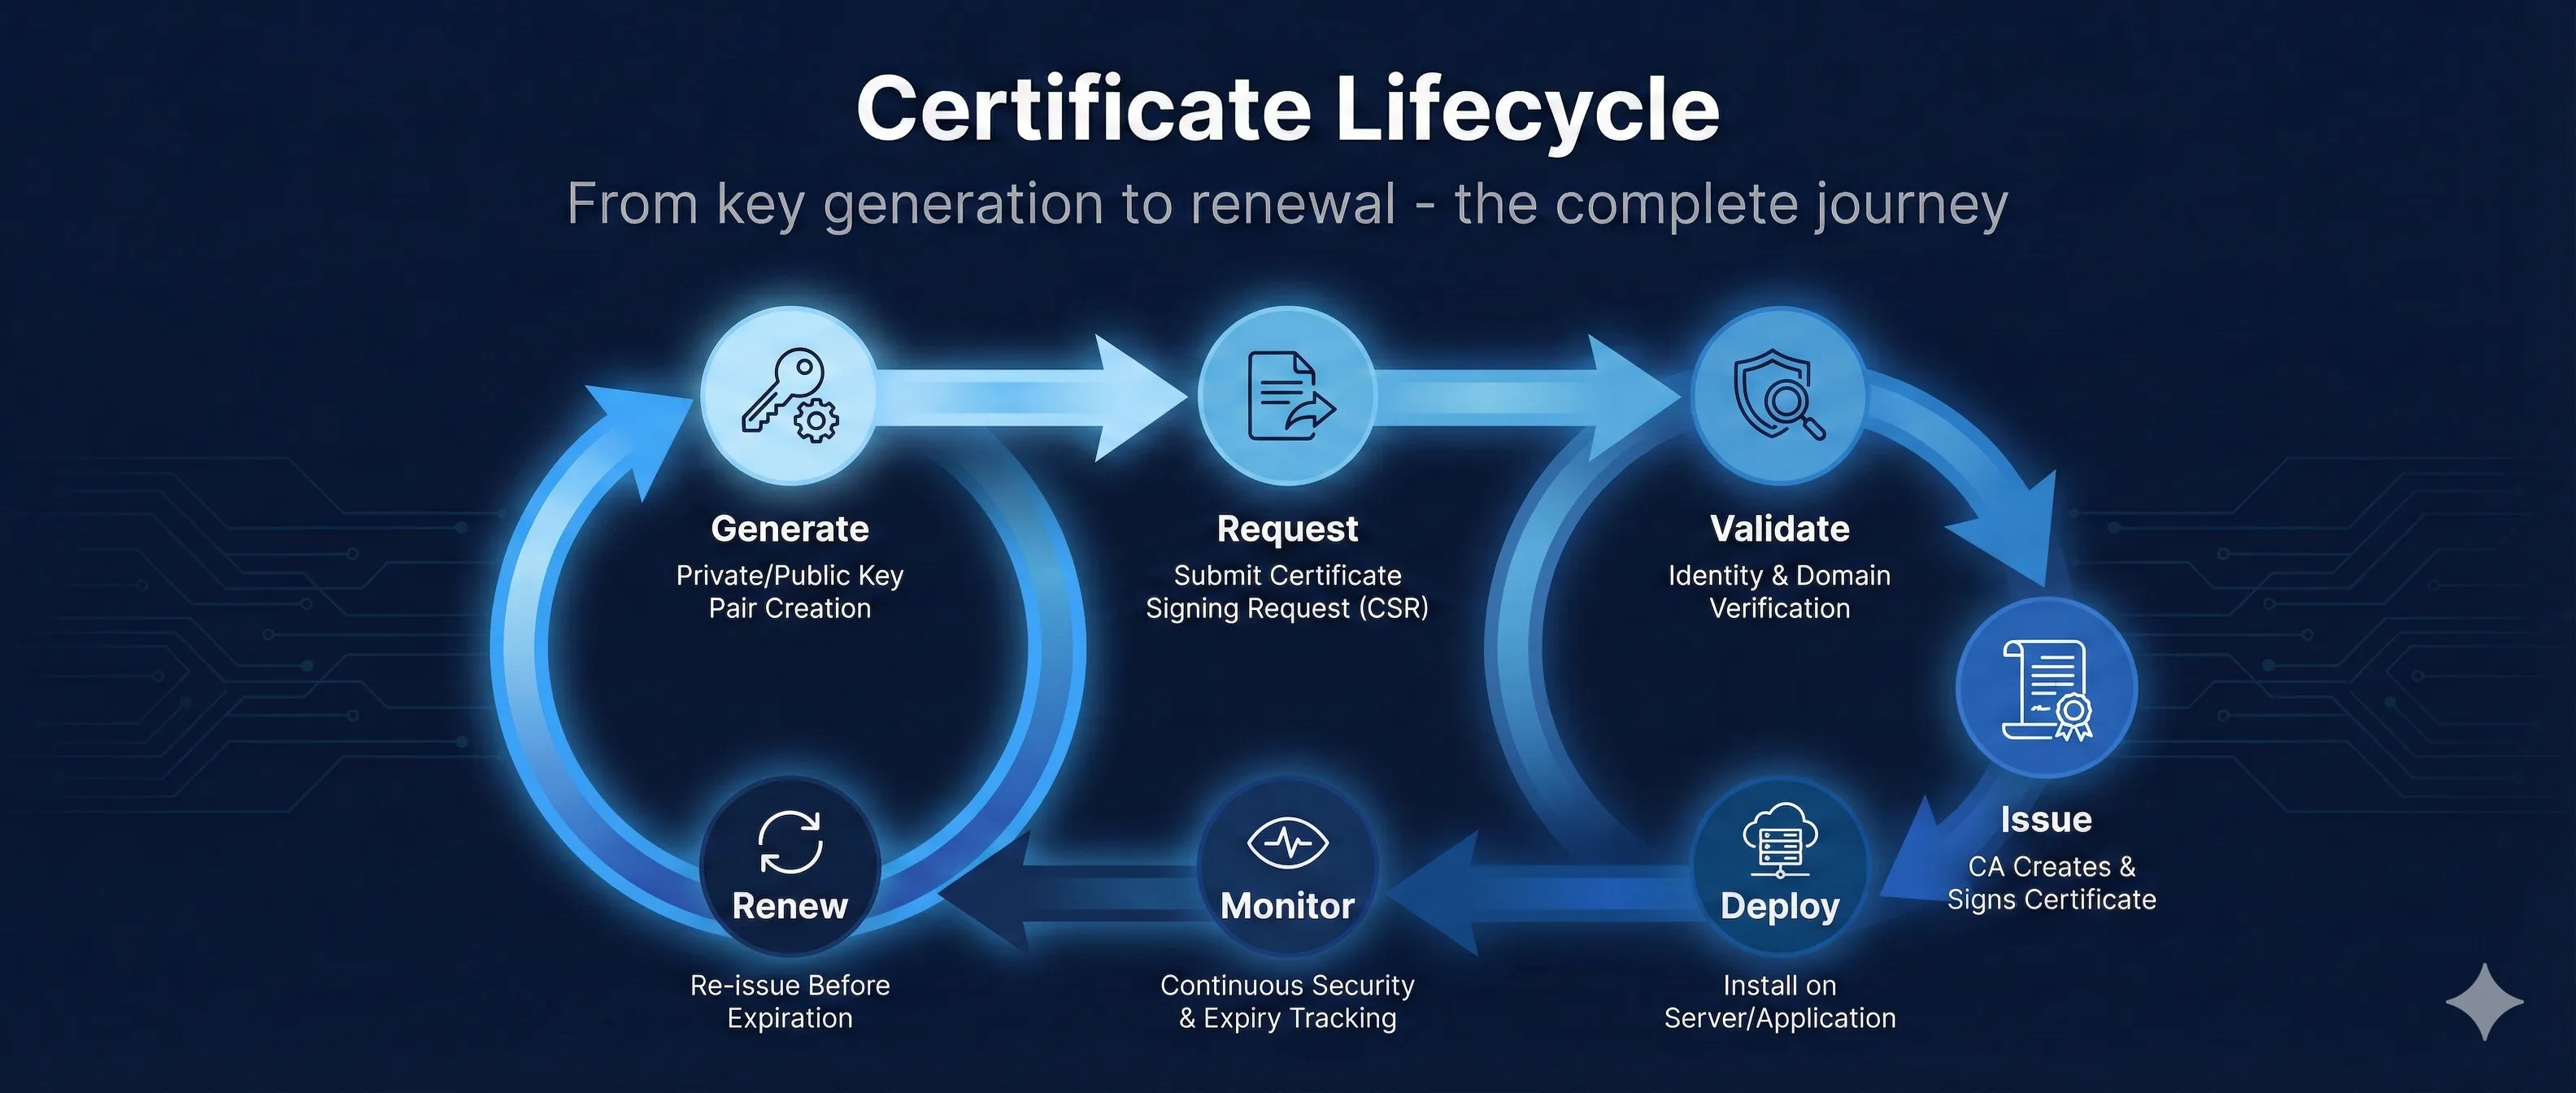
From CSR to expiration: the complete lifecycle of SSL/TLS certificates.
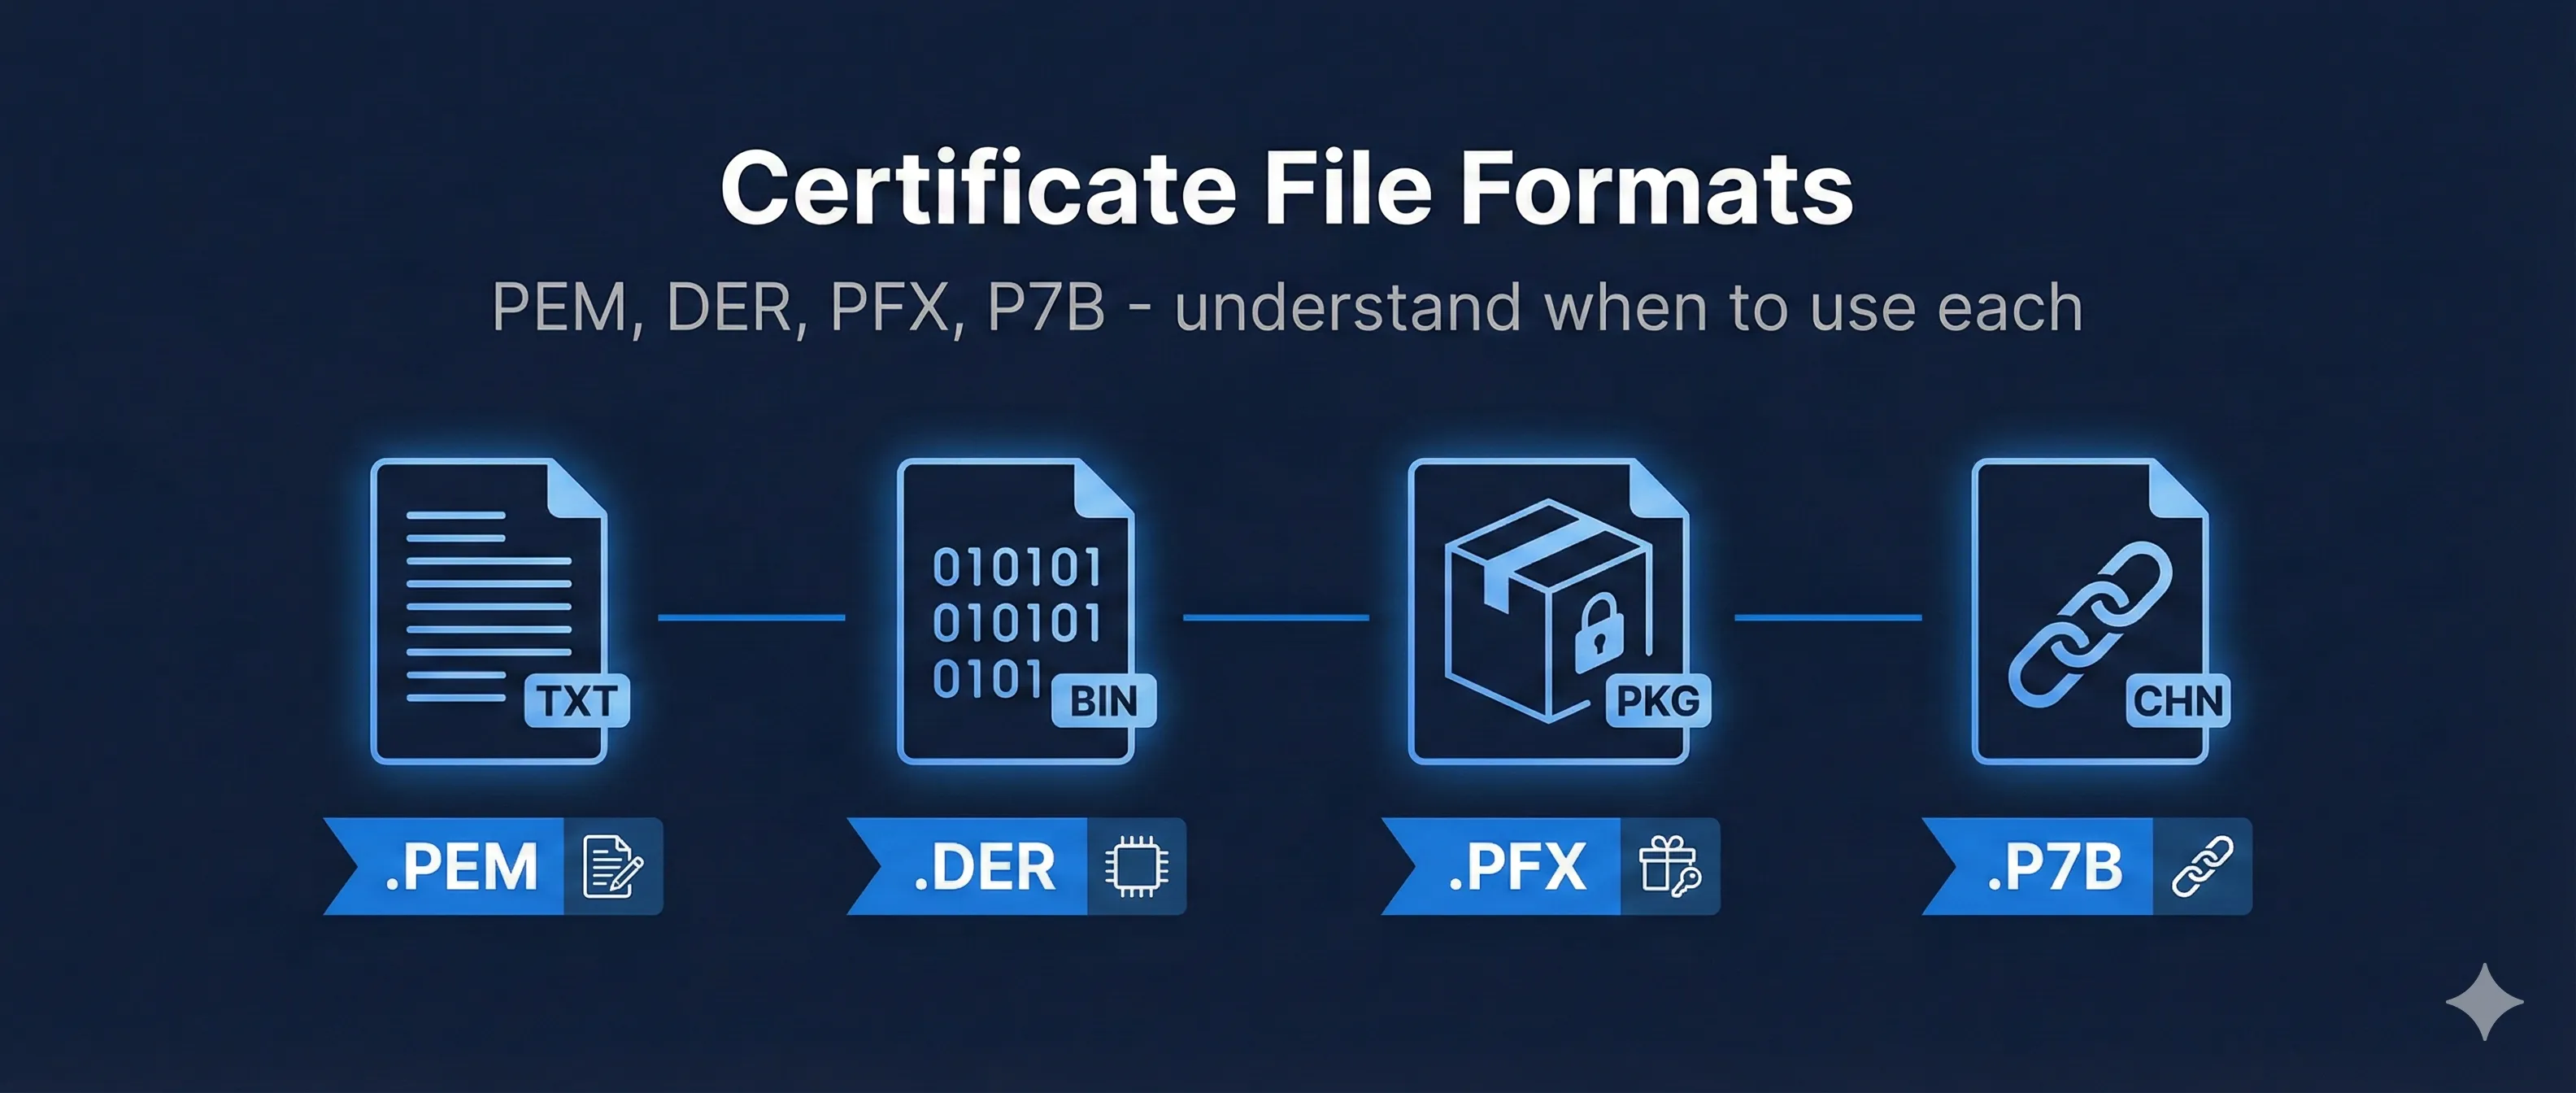
PEM, DER, PFX, JKS - understand certificate file formats and how to convert between them.
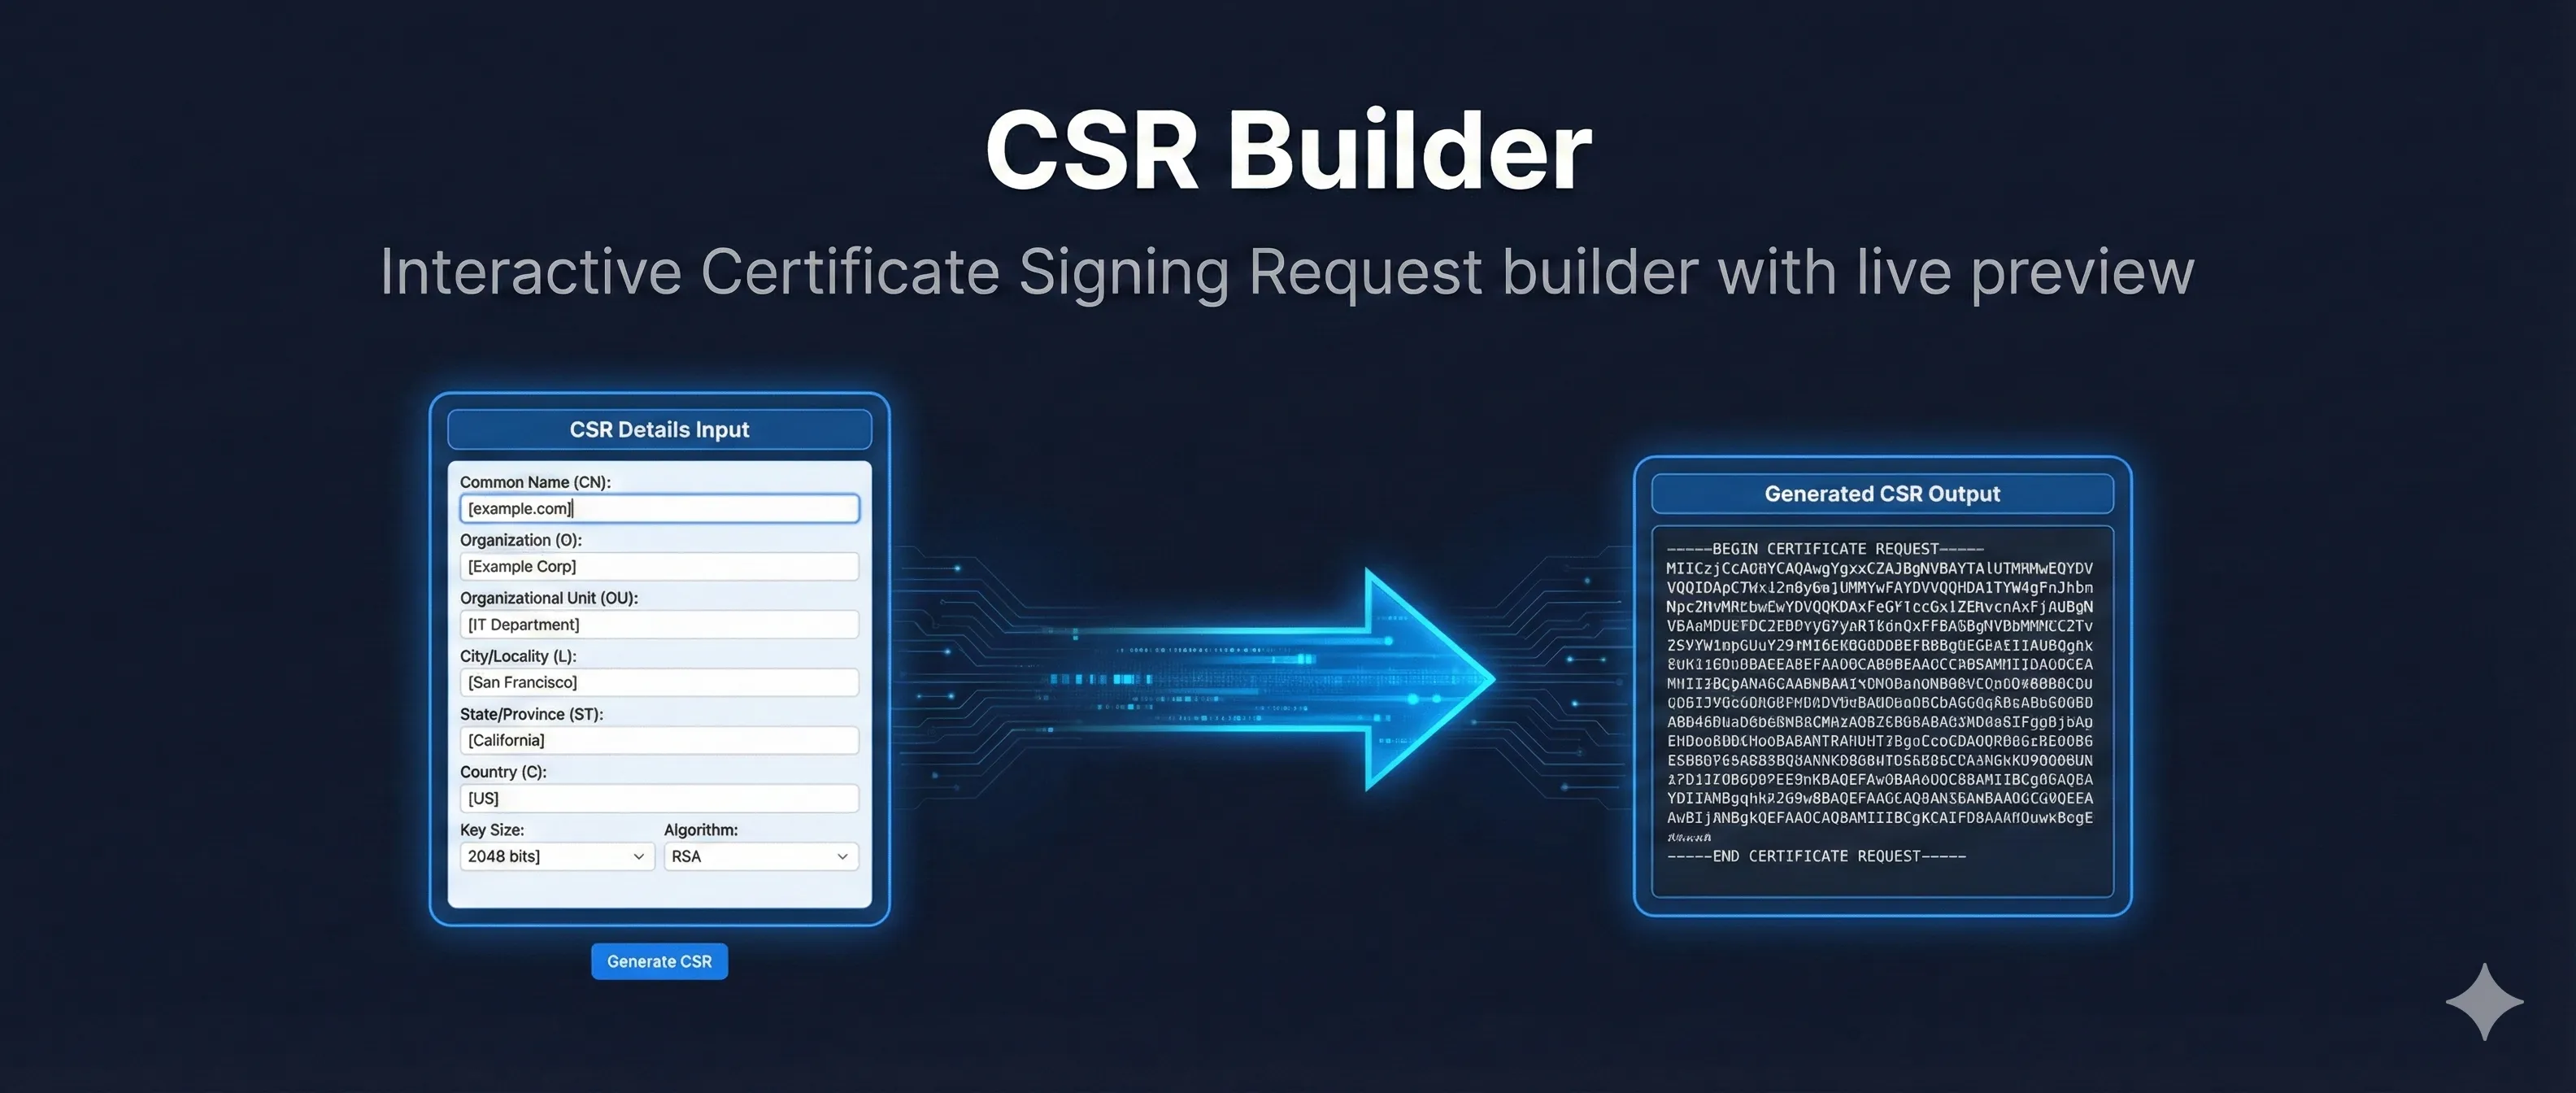
Generate Certificate Signing Requests interactively. Understand each field and extension.
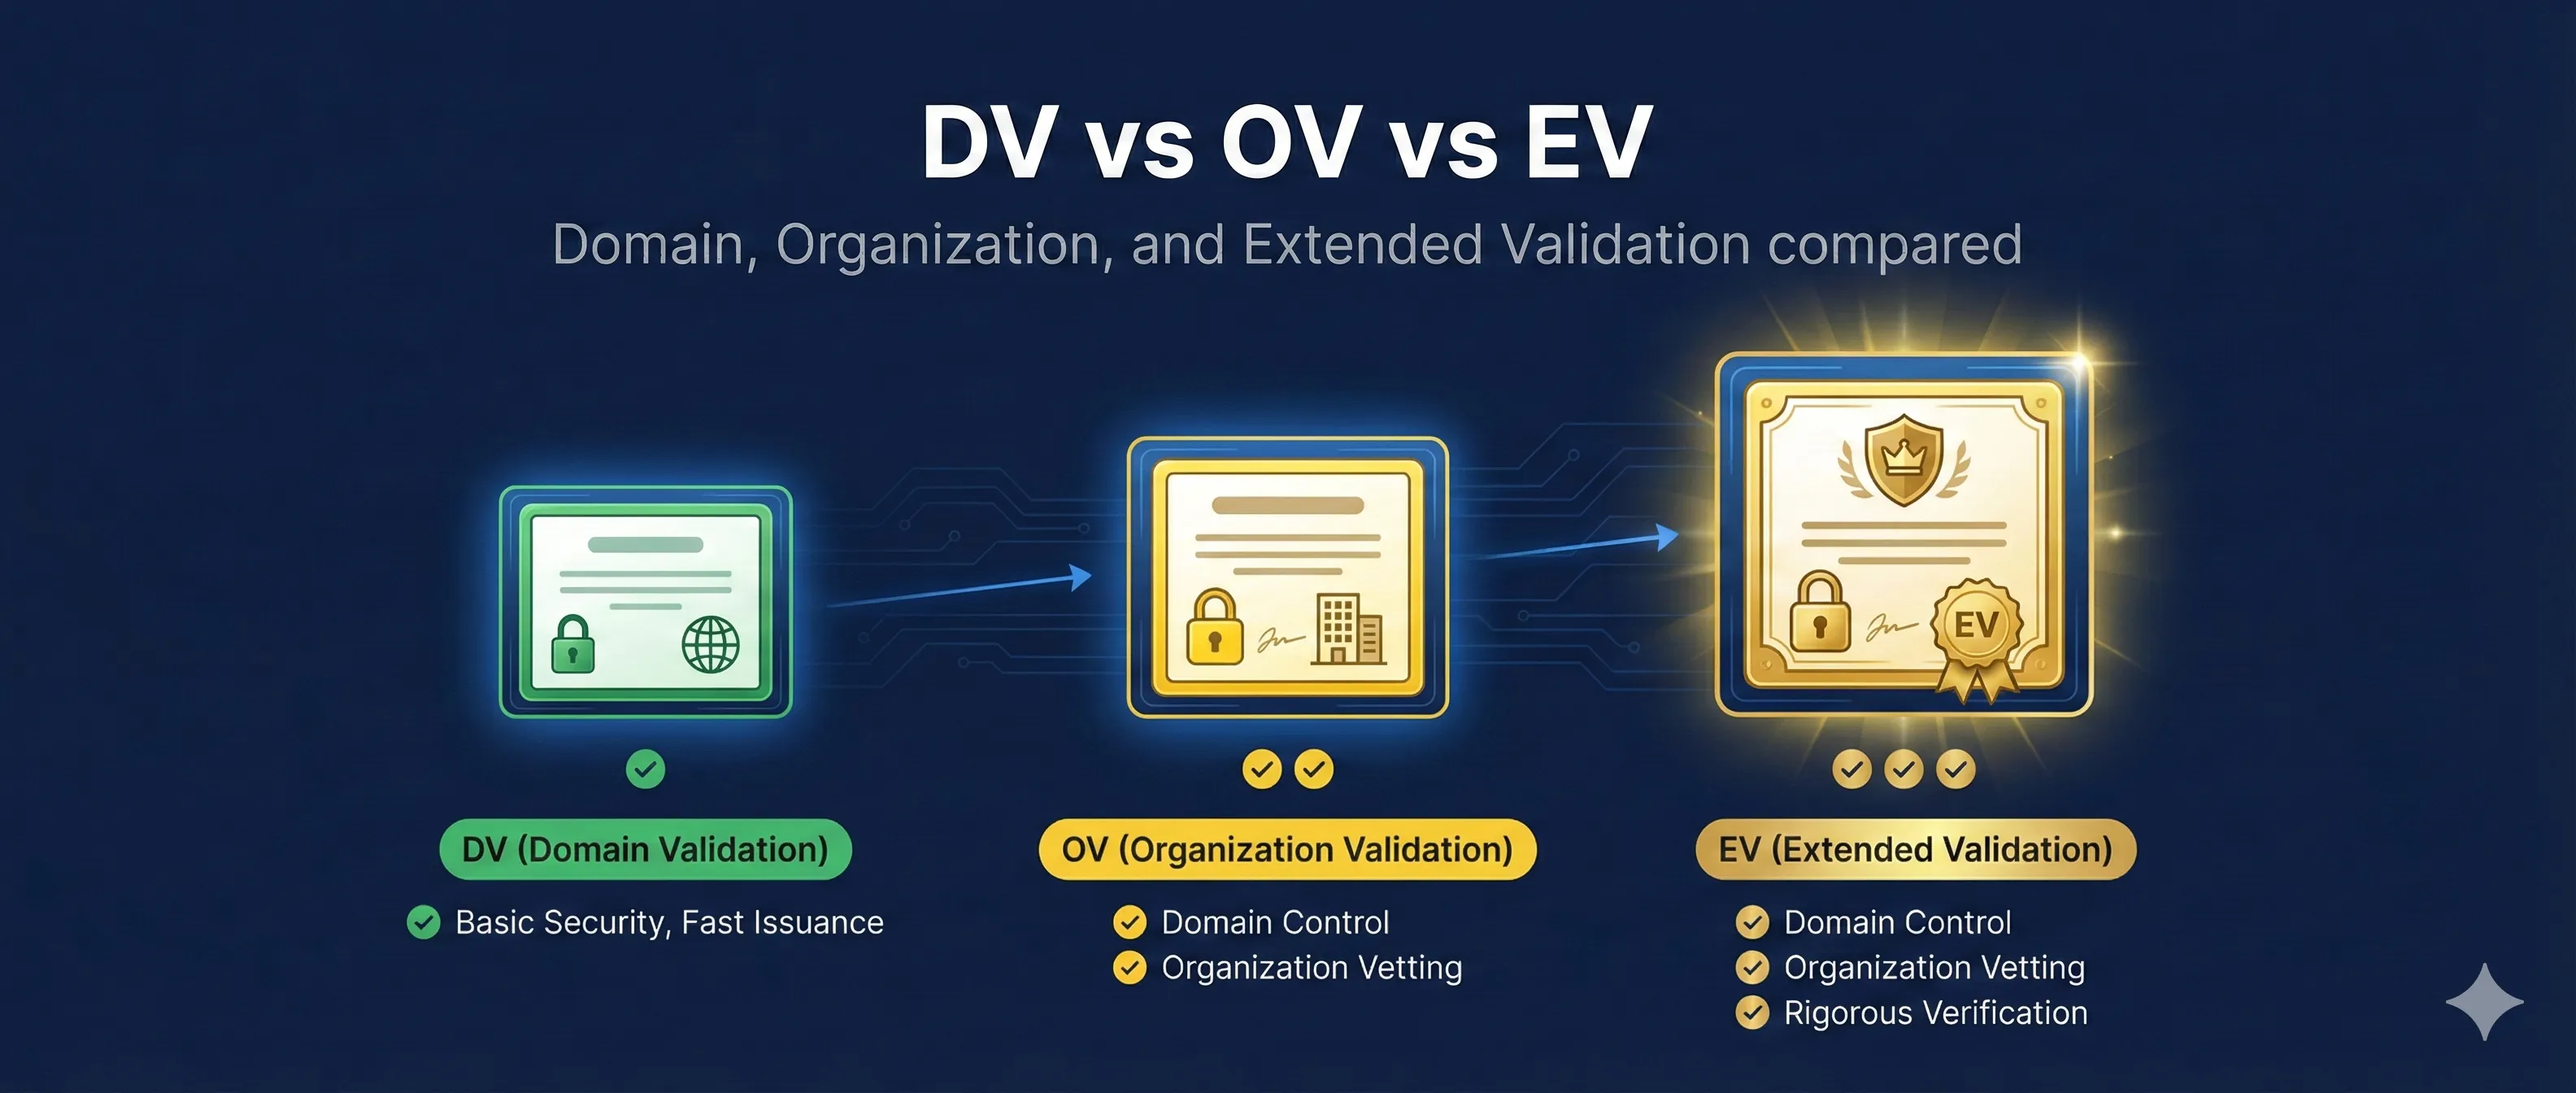
Domain, Organization, and Extended Validation certificates compared. Which do you need?
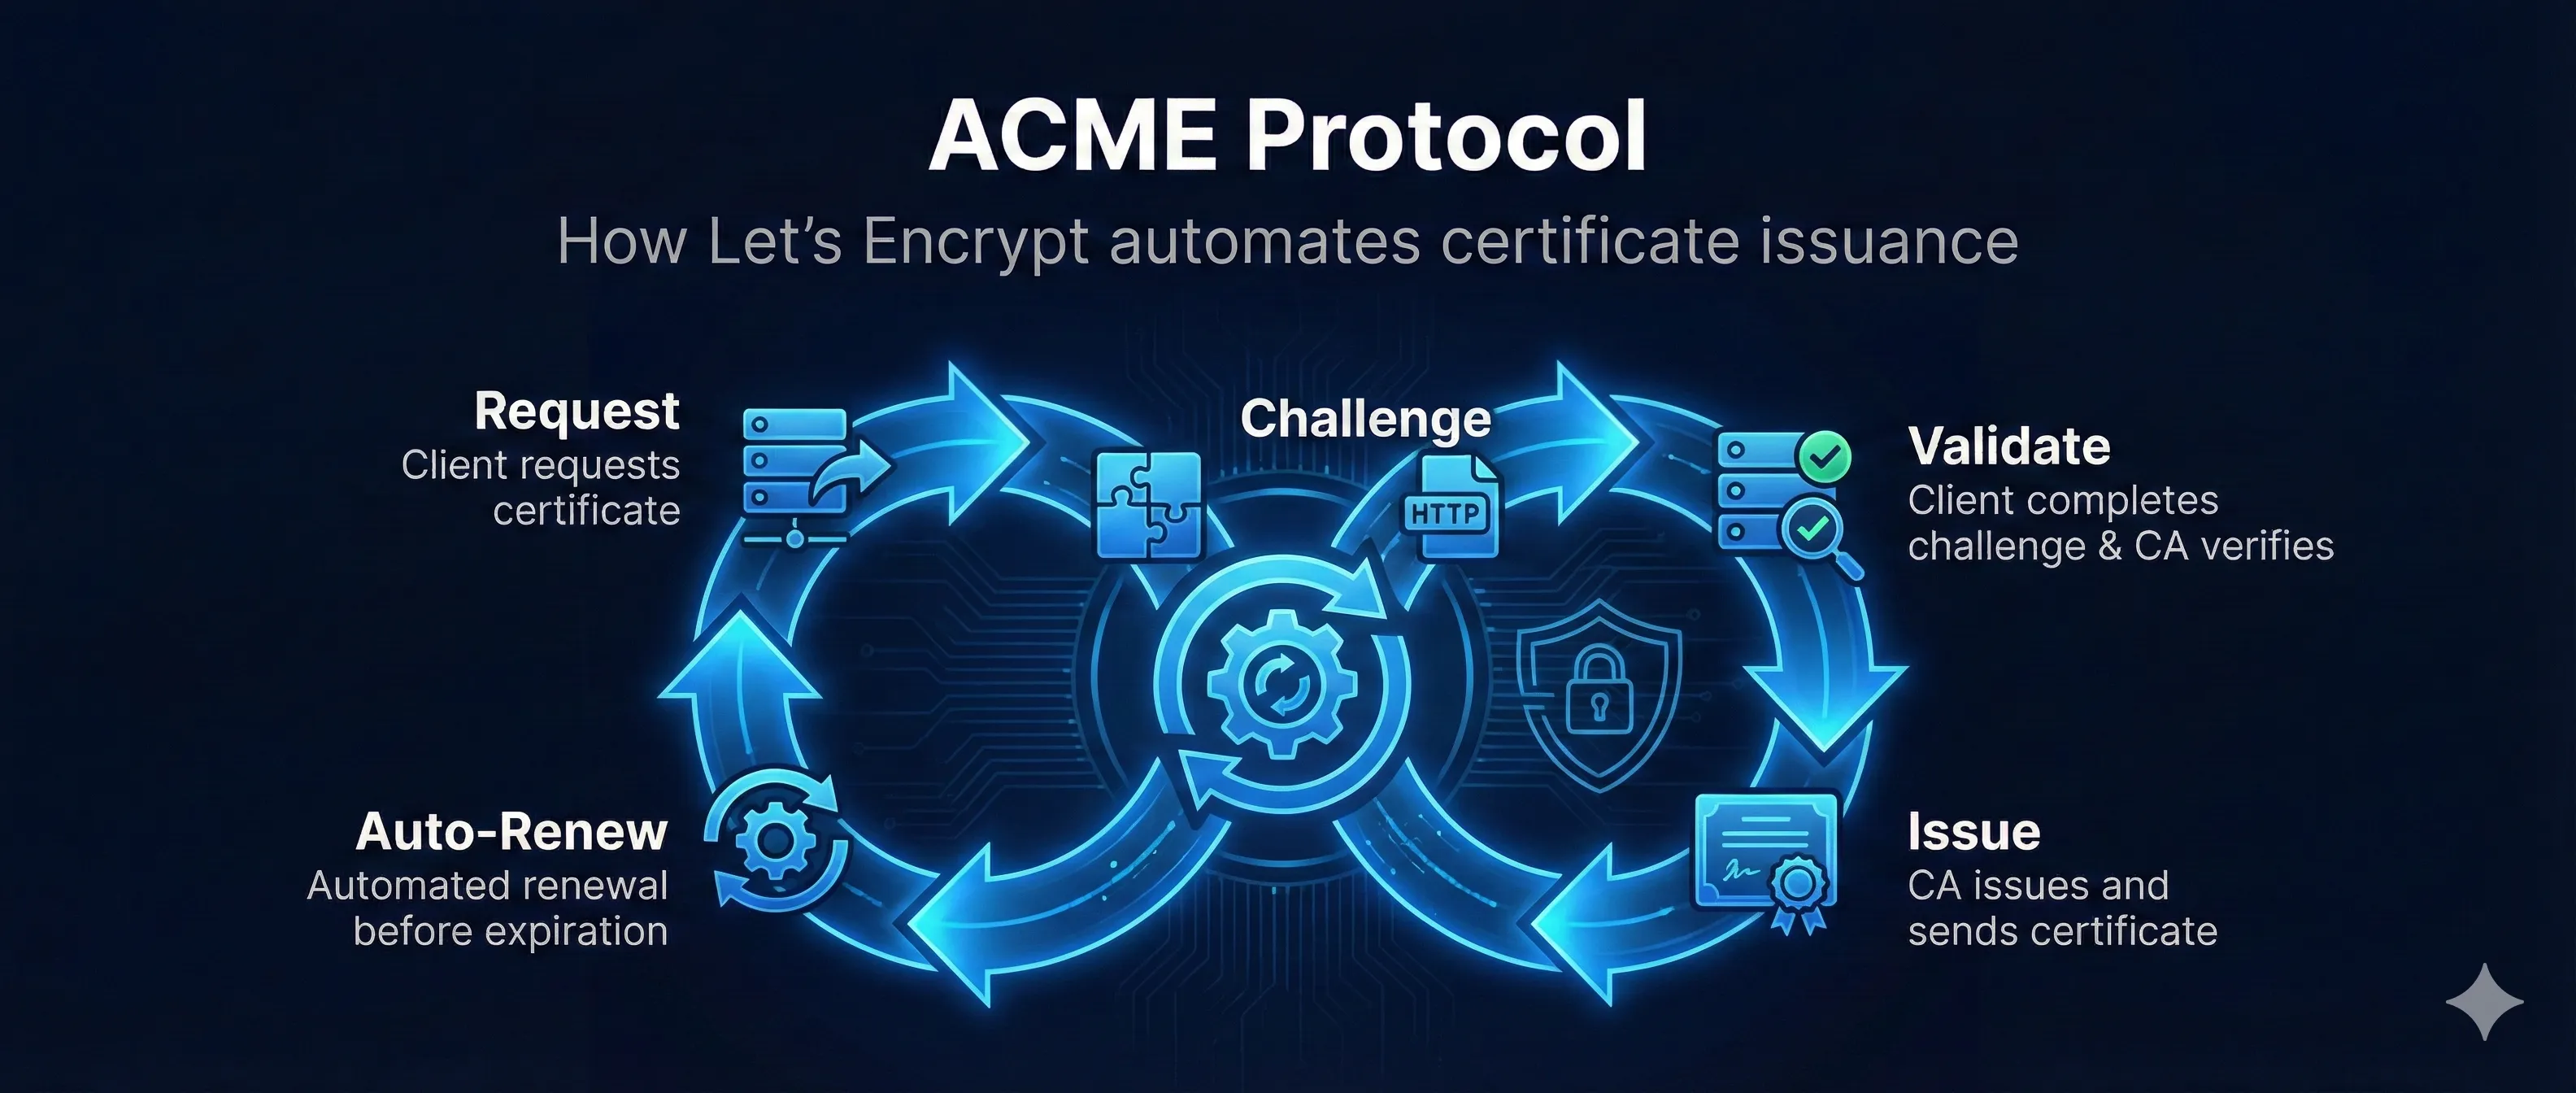
How Let's Encrypt and ACME automate certificate issuance. HTTP-01 and DNS-01 challenges explained.
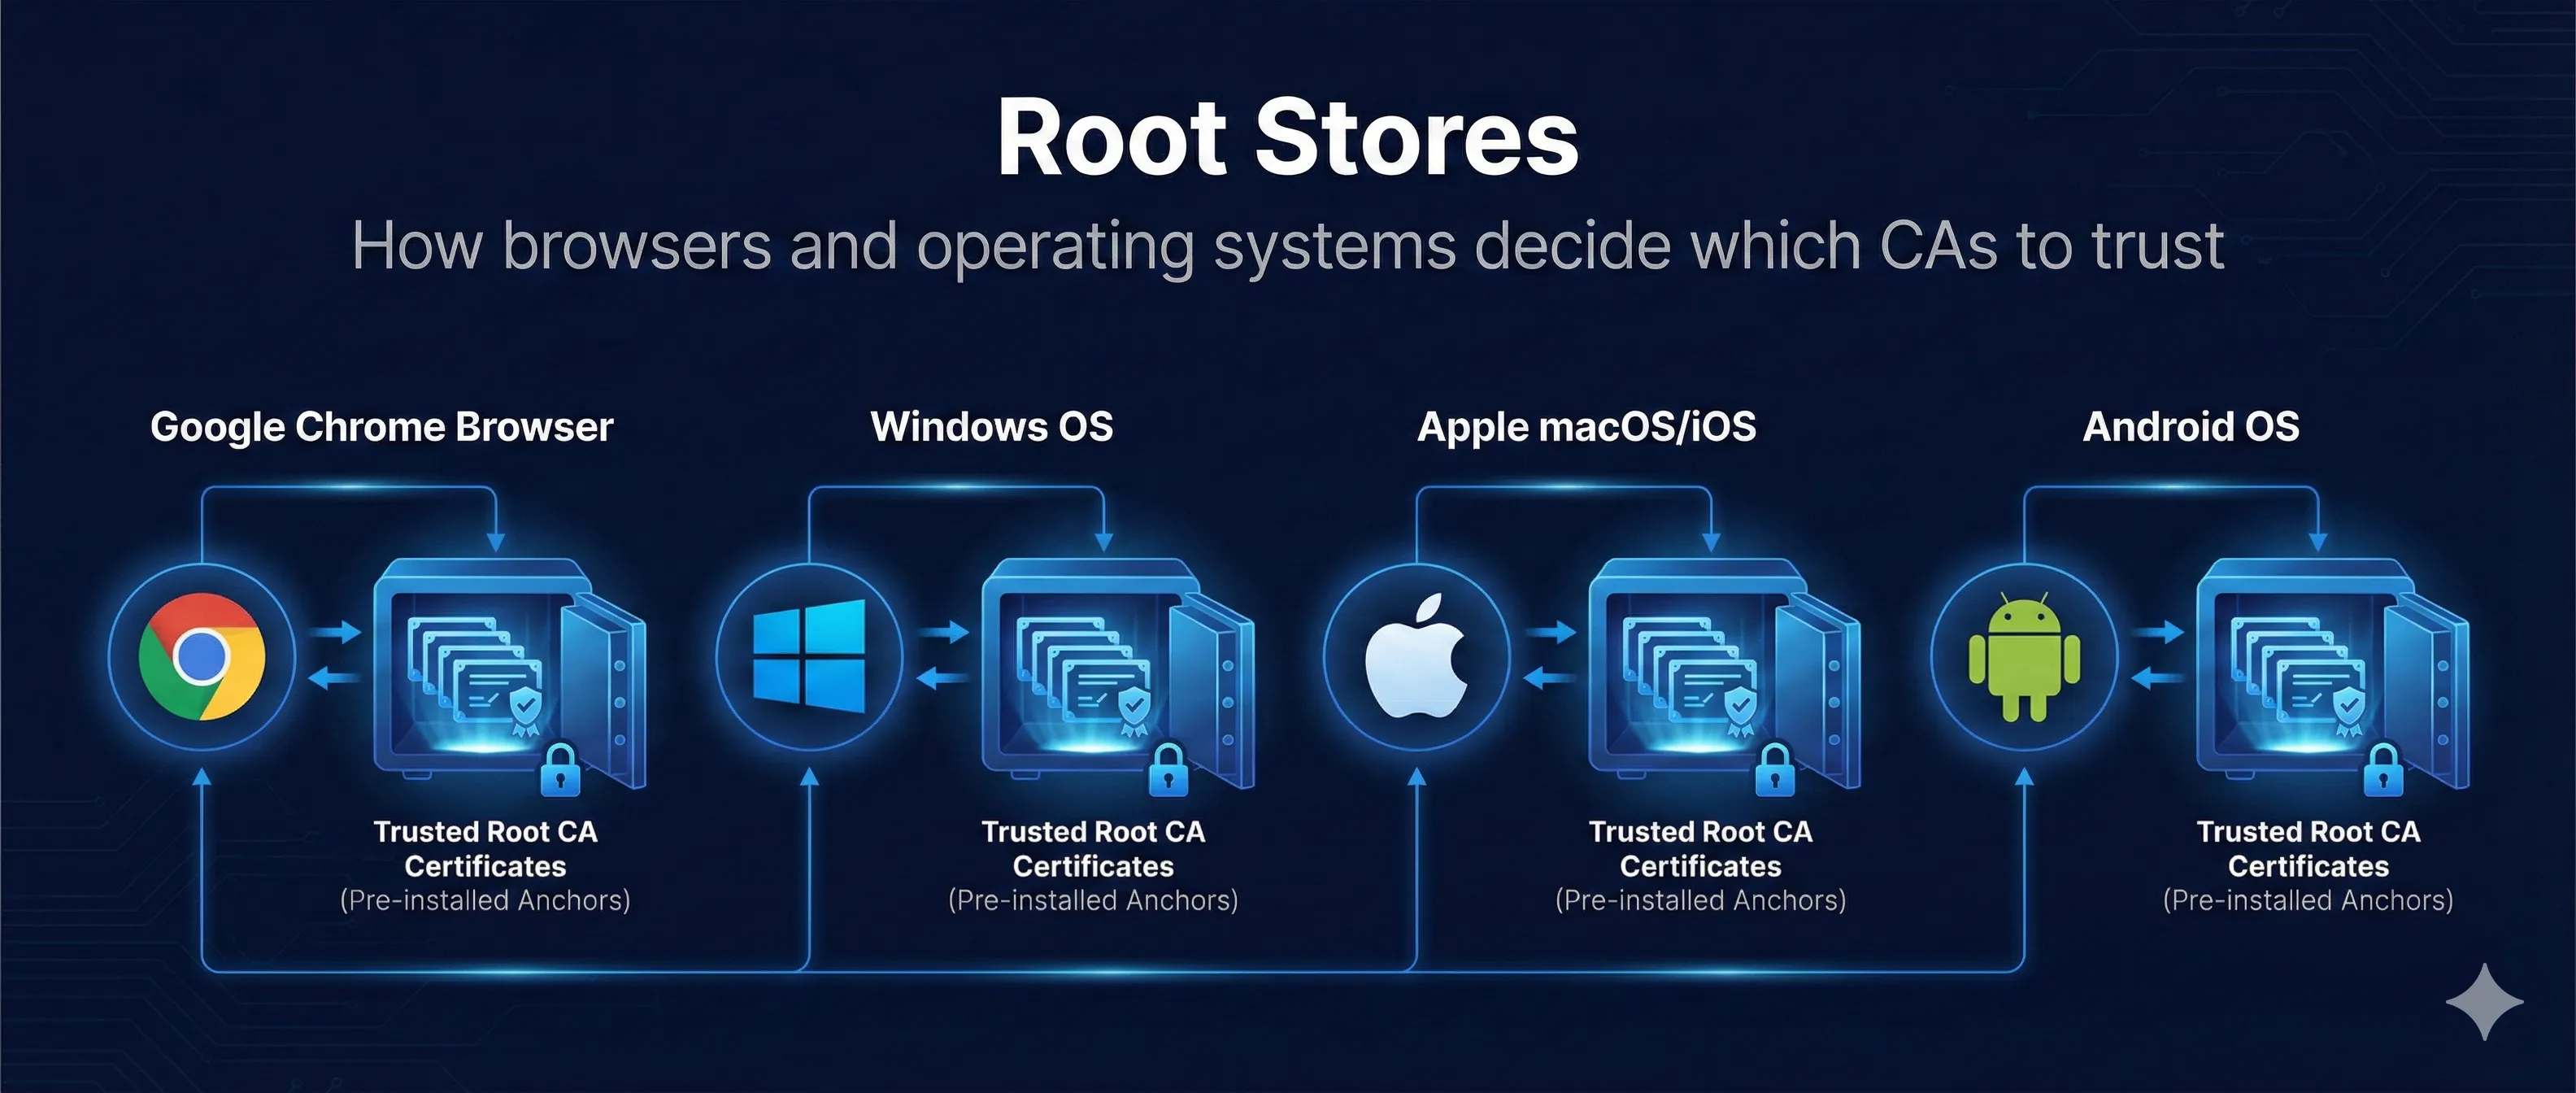
What are root stores? How browsers and operating systems decide which CAs to trust.
Baltimore CyberTrust Root expired in May 2025 and Microsoft disables it on August 27, 2026. Here's how to confirm your chain moved to DigiCert Global Root G2.
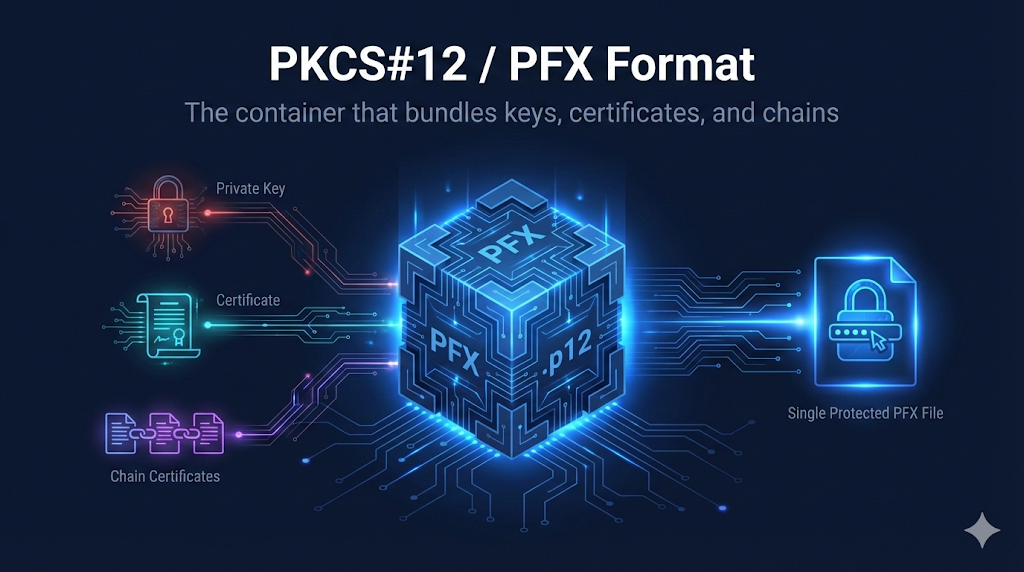
Understanding PKCS#12 format. Import, export, and manage PFX files with certificates and keys.
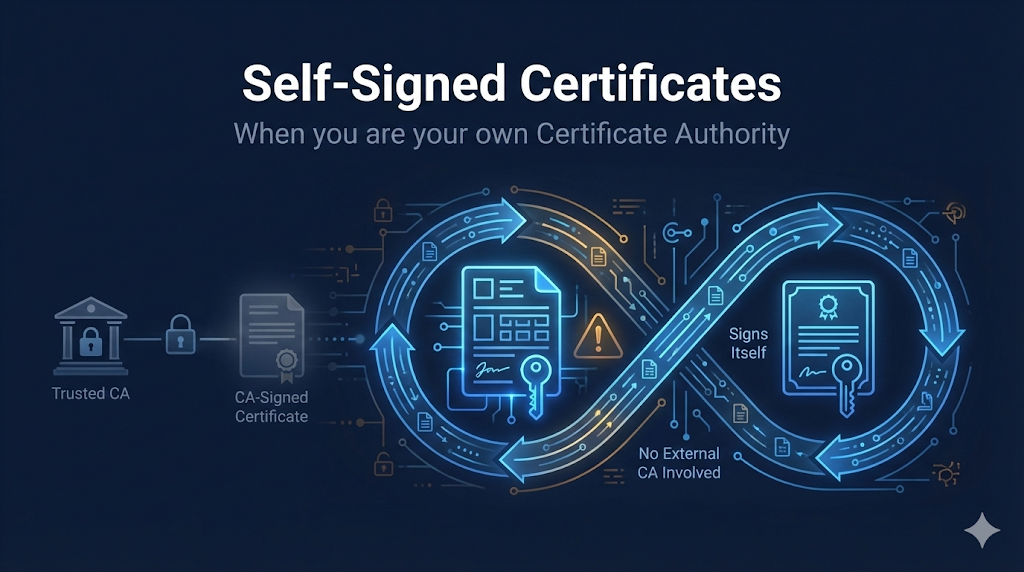
When to use self-signed certificates. Create them properly for development and internal use.
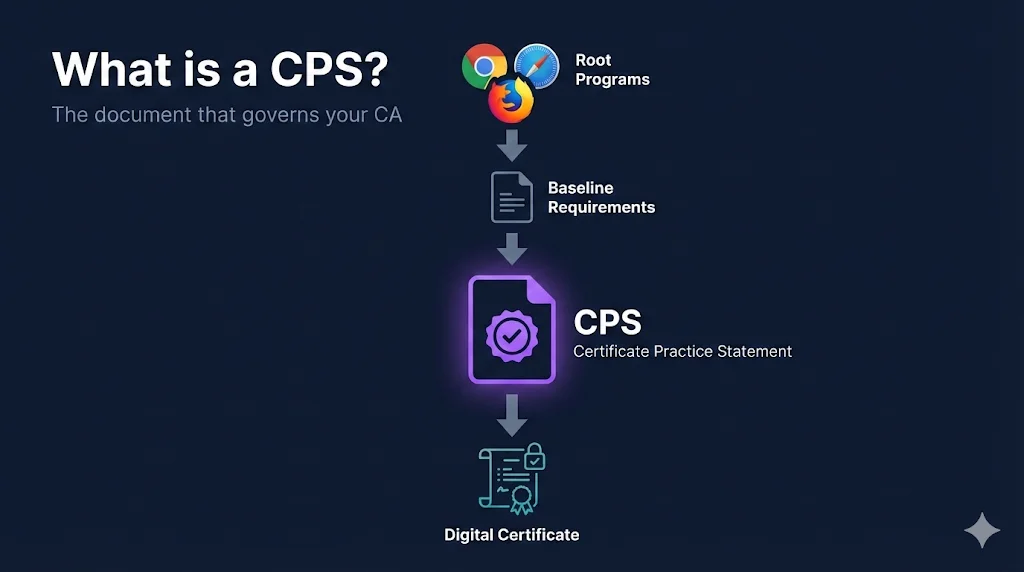
Certificate Practice Statements explained. What every PKI practitioner should know about their CA's operating procedures.
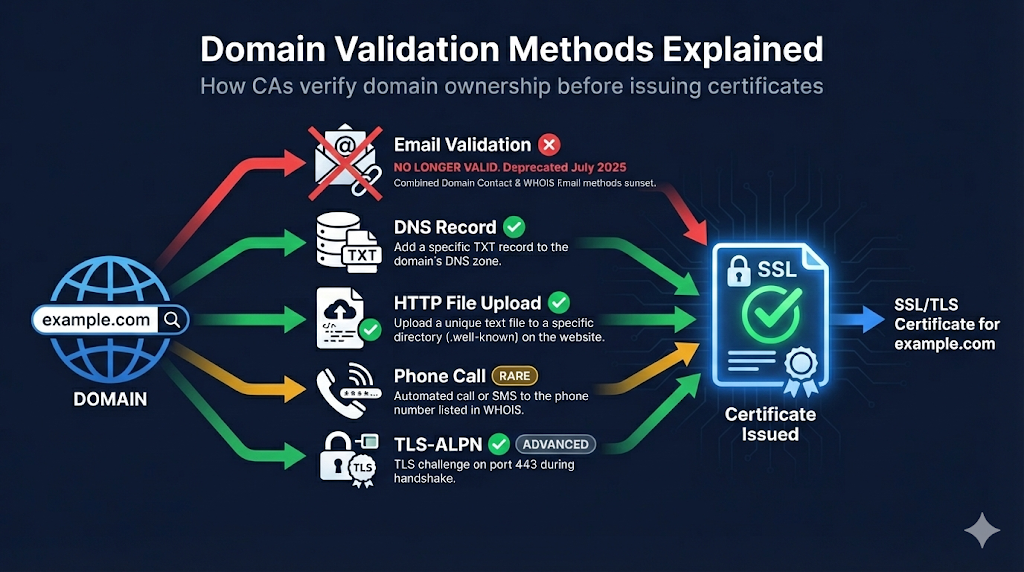
How CAs verify domain ownership before issuing certificates. All 10 approved DCV methods from CA/Browser Forum BRs.
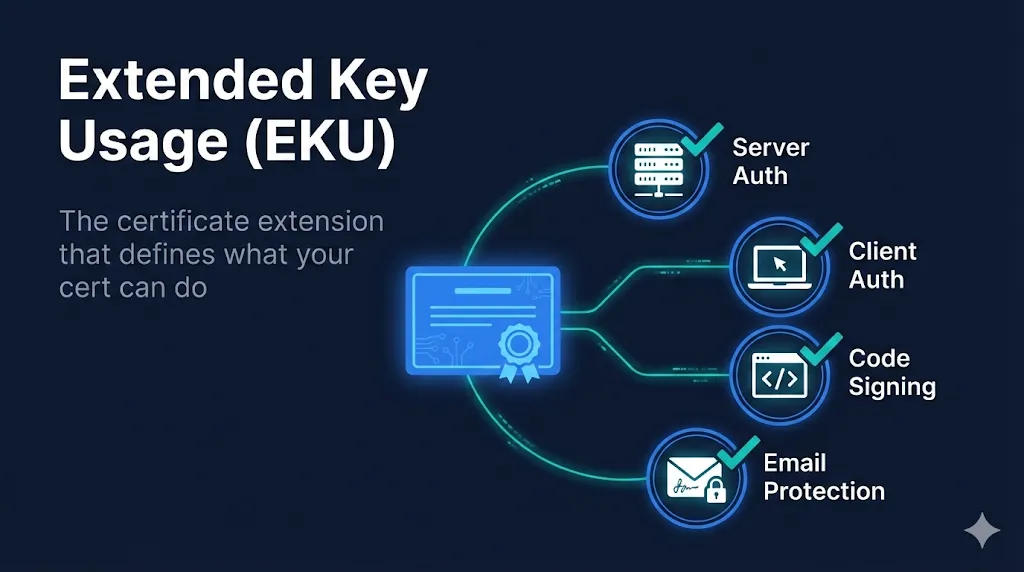
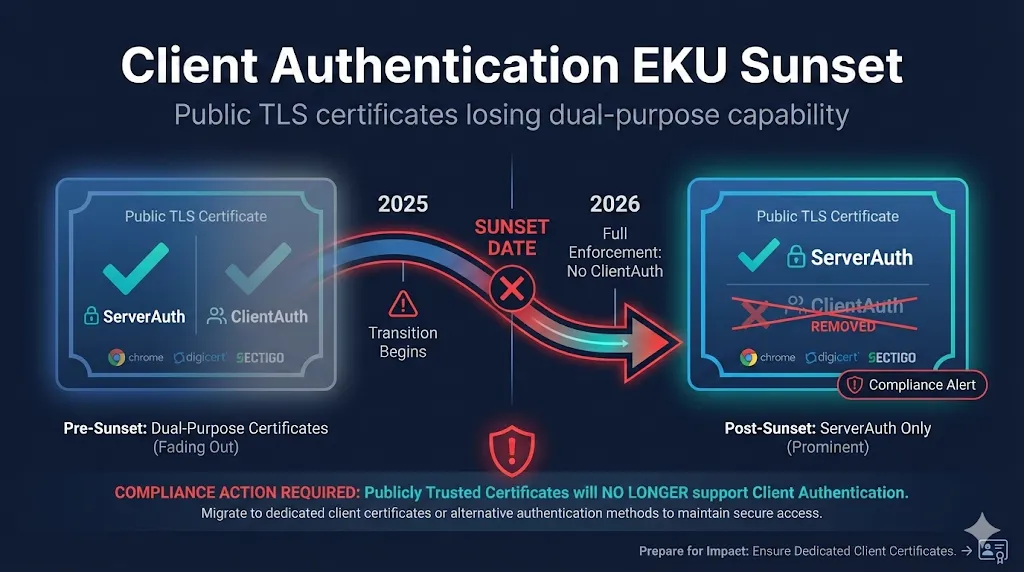
What EKU is, why it matters, and how to check yours. Covers common EKUs, OID system, and the ClientAuth sunset.
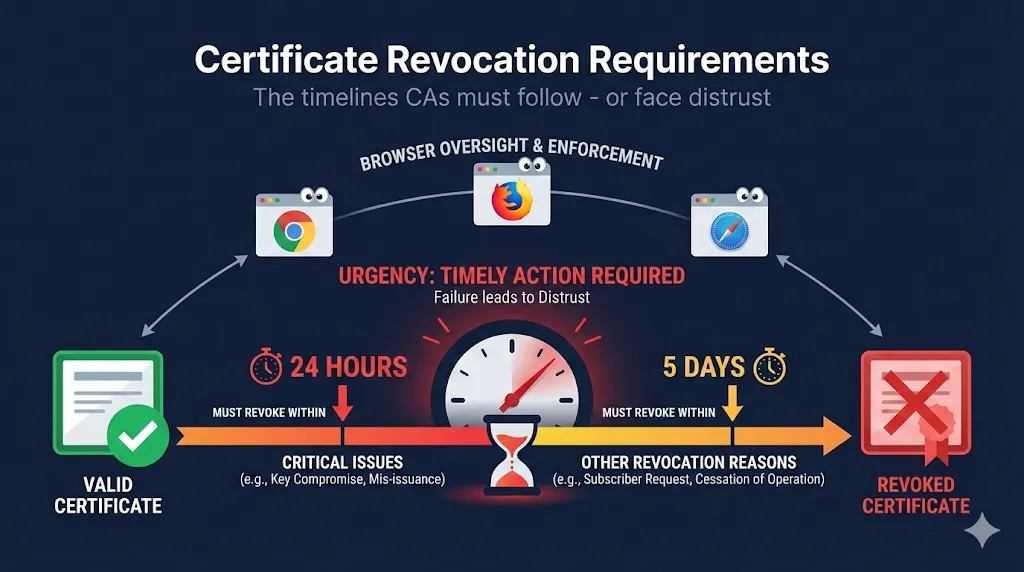
Learn the CA/Browser Forum's certificate revocation requirements - 24-hour and 5-day rules, what triggers mandatory revocation, and what happens when CAs don't comply.
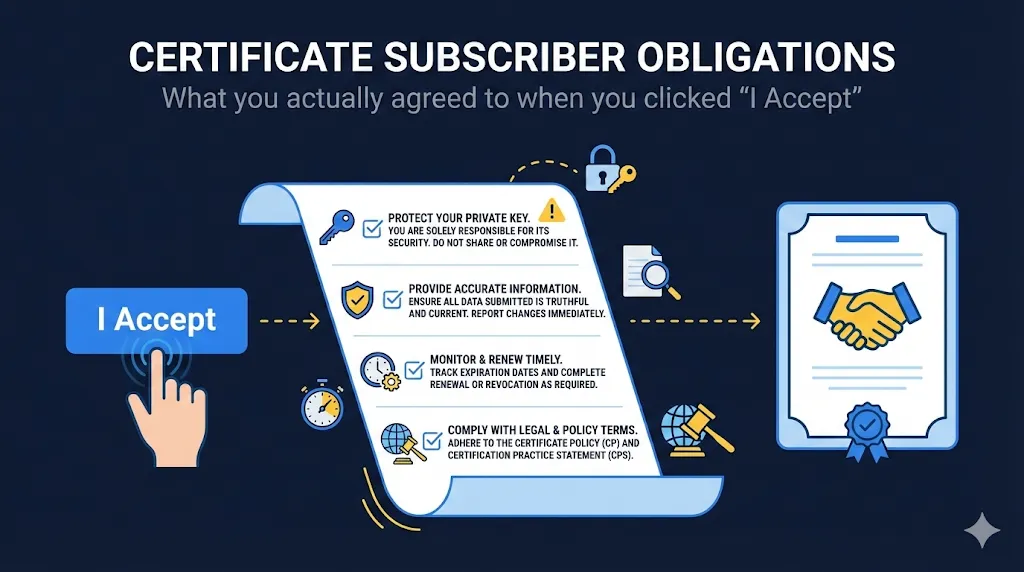
What you actually agreed to when you clicked 'I Accept' - private key protection, accuracy warranties, and what happens when you violate your subscriber agreement.
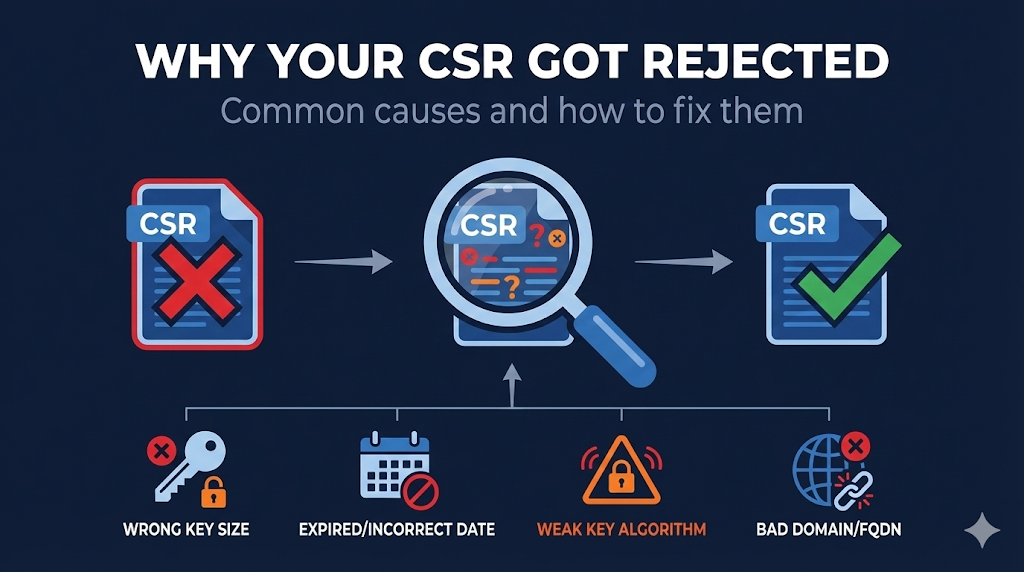
CSR rejected by your CA? Learn the common reasons certificate signing requests fail - wrong key size, weak keys, invalid domains, bad formatting - and how to fix each one.
Pin certificate issuance to your ACME account and validation method using RFC 8657 accounturi and validationmethods parameters. Mandatory March 15, 2027 under SC-098v2.
Chrome and major CAs are removing Client Authentication EKU from public TLS certificates by March 2027. Learn who's affected, key deadlines, and migration options.
Public CAs are removing the clientAuth EKU by March 2027. Here is how to find every client authentication certificate in your environment before renewals break.